|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200501-39] SquirrelMail: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200501-39] SquirrelMail: Multiple vulnerabilities |
||
|
SquirrelMail: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200501-39 (SquirrelMail: Multiple vulnerabilities) SquirrelMail fails to properly sanitize certain strings when decoding specially-crafted strings, which can lead to PHP file inclusion and XSS. Insufficient checking of incoming URLs in prefs.php (CVE-2005-0075) and in webmail.php (CVE-2005-0103). Insufficient escaping of integers in webmail.php (CVE-2005-0104). Impact By sending a specially-crafted URL, a possible hacker can execute arbitrary code from the local system with the permissions of the web server. Furthermore by enticing a user to load a specially-crafted URL, it is possible to display arbitrary remote web pages in Squirrelmail's frameset and execute arbitrary scripts running in the context of the victim's browser. This could lead to a compromise of the user's webmail account, cookie theft, etc. Workaround The arbitrary code execution is only possible with "register_globals" set to "On". Gentoo ships PHP with "register_globals" set to "Off" by default. There are no known workarounds for the other issues at this time. References: http://sourceforge.net/mailarchive/message.php?msg_id=10628451 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0075 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0103 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0104 Solution: All SquirrelMail users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=mail-client/squirrelmail-1.4.4" Note: Users with the vhosts USE flag set should manually use webapp-config to finalize the update. Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

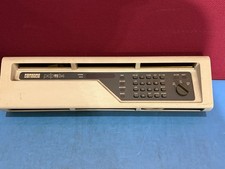
DEC PDP-11/34 Front Panel Complete PDP11 RARE
$450.00
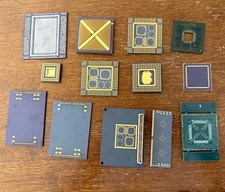
Vintage Intel Mainframe Server MCM CPU Substrate Lot Prototyping PGA Validation
$500.00
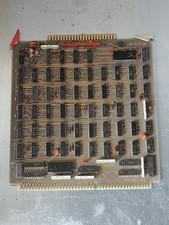
HP 13210-60001 Disc Drive Interface PCB HP 7900A 7901A Vintage
$225.61
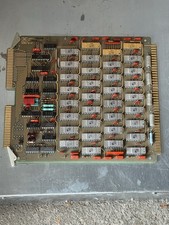
HP 5060-8359 8K Semiconductor Memory Module 5080-9747 Vintage HP Computer
$224.72
Vtg IBM Mainframe Prototype Chip Module Lot 146 pc 1988-1993 ES/9000 Lab Arcive
$649.00
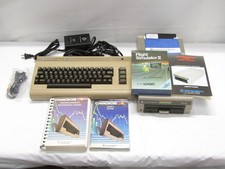
Commodore 64 PC with Model 1541 Diskette Drive and Flight Simulator II *READ*
$199.99
Vintage Mainframe Computer Disk Drive Pack Dyson SMD 5 Level Disks
$79.00
Rare Vintage Mainframe Burroughs Discrete-Transistor Cordwood Module B2500/B5000
$99.95
Vintage Telex 952003-112 Mechanical Terminal Keyboard IBM 3270 Mainframe DB25
$799.00
Vintage UNIVAC 3620670-01 Mainframe Logic Board 15MHz Sperry Computer PCB
$98.95
|
||
|
No Discussions have been posted on this vulnerability. |