|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200501-31] teTeX, pTeX, CSTeX: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200501-31] teTeX, pTeX, CSTeX: Multiple vulnerabilities |
||
|
teTeX, pTeX, CSTeX: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200501-31 (teTeX, pTeX, CSTeX: Multiple vulnerabilities) teTeX, pTeX and CSTeX all make use of Xpdf code and may therefore be vulnerable to the various overflows that were discovered in Xpdf code (CVE-2004-0888, CVE-2004-0889, CVE-2004-1125 and CVE-2005-0064). Furthermore, Javier Fernandez-Sanguino Pena discovered that the xdvizilla script does not handle temporary files correctly. Impact A possible hacker could design a malicious input file which, when processed using one of the TeX distributions, could lead to the execution of arbitrary code. Furthermore, a local attacker could create symbolic links in the temporary files directory, pointing to a valid file somewhere on the filesystem. When xdvizilla is called, this would result in the file being overwritten with the rights of the user running the script. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0888 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0889 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1125 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0064 Solution: All teTeX users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-text/tetex-2.0.2-r5" All CSTeX users should also upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-text/cstetex-2.0.2-r1" Finally, all pTeX users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=app-text/ptex-3.1.4-r2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

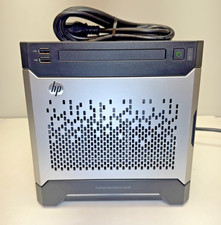
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro CSE-815-5 4B LFF Xeon E3-1245v6 16GB DDR4 1x 9361-8i 4x 1TB SATA HDD
$483.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |