|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200501-25] Squid: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200501-25] Squid: Multiple vulnerabilities |
||
|
Squid: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200501-25 (Squid: Multiple vulnerabilities) Squid contains a vulnerability in the gopherToHTML function (CVE-2005-0094) and incorrectly checks the 'number of caches' field when parsing WCCP_I_SEE_YOU messages (CVE-2005-0095). Furthermore the NTLM code contains two errors. One is a memory leak in the fakeauth_auth helper (CVE-2005-0096) and the other is a NULL pointer dereferencing error (CVE-2005-0097). Finally Squid also contains an error in the ACL parsing code (CVE-2005-0194). Impact With the WCCP issue a possible hacker could cause denial of service by sending a specially crafted UDP packet. With the Gopher issue an attacker might be able to execute arbitrary code by enticing a user to connect to a malicious Gopher server. The NTLM issues could lead to denial of service by memory consumption or by crashing Squid. The ACL issue could lead to ACL bypass. Workaround There is no known workaround at this time. References: http://secunia.com/advisories/13825/ http://secunia.com/advisories/13789/ http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0094 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0095 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0096 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0097 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-0194 Solution: All Squid users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=www-proxy/squid-2.5.7-r2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
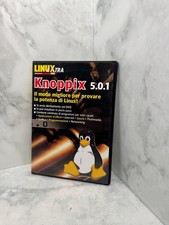
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |