|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200412-25] CUPS: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200412-25] CUPS: Multiple vulnerabilities |
||
|
CUPS: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200412-25 (CUPS: Multiple vulnerabilities) CUPS makes use of vulnerable Xpdf code to handle PDF files (CVE-2004-1125). Furthermore, Ariel Berkman discovered a buffer overflow in the ParseCommand function in hpgl-input.c in the hpgltops program (CVE-2004-1267). Finally, Bartlomiej Sieka discovered several problems in the lppasswd program: it ignores some write errors (CVE-2004-1268), it can leave the passwd.new file in place (CVE-2004-1269) and it does not verify that passwd.new file is different from STDERR (CVE-2004-1270). Impact The Xpdf and hpgltops vulnerabilities may be exploited by a remote attacker to execute arbitrary code by sending specific print jobs to a CUPS spooler. The lppasswd vulnerabilities may be exploited by a local attacker to write data to the CUPS password file or deny further password modifications. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1125 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1267 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1268 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1269 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-1270 http://tigger.uic.edu/~jlongs2/holes/cups.txt http://tigger.uic.edu/~jlongs2/holes/cups2.txt Solution: All CUPS users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=net-print/cups-1.1.23" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

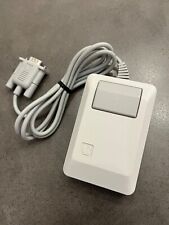
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$49.99
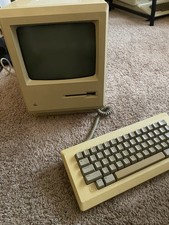
Apple Macintosh 128k Desktop computer. Upgraded to 512k
$300.00
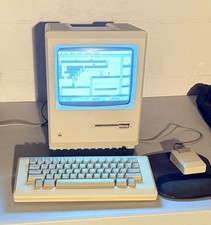
1984 APPLE MACINTOSH 128K MATCHING # BOX Set Original Mac Model M0001 WORKS RARE
$6299.00

1984 APPLE MACINTOSH 128K FIRST MAC Model M0001 PICASSO KIT Discs Harvard Rare
$1800.00
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$59.99
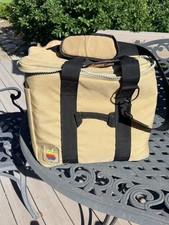
Vintage Apple Macintosh 128K 512K Carrying Case Rainbow Logo Excellent Cond
$140.00
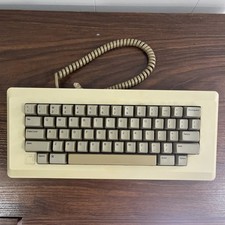
Apple Keyboard and Cable for Macintosh 128k 512k Mac Plus RARE Vintage M0110
$129.99
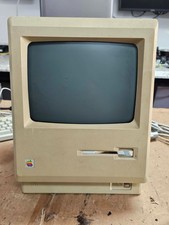
Vintage Early Week 12 1984 Apple Macintosh 128K Computer M0001 w/Analog Board+
$209.99
Apple Keyboard for Macintosh 128k 512k Mac Plus RARE Vintage M0110 (010)
$149.00
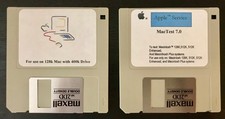
Apple Macintosh Mac 128k - 512k Boot / Diagnostics 2 Disk Set for Classic Macs
$14.99
|
||
|
No Discussions have been posted on this vulnerability. |