|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200412-17] kfax: Multiple overflows in the included TIFF library Vulnerability Assessment Details
|
[GLSA-200412-17] kfax: Multiple overflows in the included TIFF library |
||
|
kfax: Multiple overflows in the included TIFF library Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200412-17 (kfax: Multiple overflows in the included TIFF library) Than Ngo discovered that kfax contains a private copy of the TIFF library and is therefore subject to several known vulnerabilities (see References). Impact A remote attacker could entice a user to view a carefully-crafted TIFF image file with kfax, which would potentially lead to execution of arbitrary code with the rights of the user running kfax. Workaround The KDE Team recommends to remove the kfax binary as well as the kfaxpart.la KPart: rm /usr/kde/3.*/lib/kde3/kfaxpart.la rm /usr/kde/3.*/bin/kfax Note: This will render the kfax functionality useless, if kfax functionality is needed you should upgrade to the KDE 3.3.2 which is not stable at the time of this writing. There is no known workaround at this time. References: http://www.kde.org/info/security/advisory-20041209-2.txt http://www.gentoo.org/security/en/glsa/glsa-200410-11.xml http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0803 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0804 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0886 Solution: All kfax users should upgrade to the latest version: # emerge --sync # emerge --ask --oneshot --verbose ">=kde-base/kdegraphics-3.3.2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
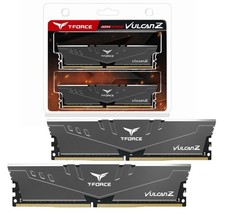
TeamGroup T-FORCE VULCAN Z 16GB (2 x 8GB) DDR4 3000Mz (PC4 24000) Desktop Memory
$97.76
|
||
|
No Discussions have been posted on this vulnerability. |