|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200409-26] Mozilla, Firefox, Thunderbird, Epiphany: New releases fix vulnerabilities Vulnerability Assessment Details
|
[GLSA-200409-26] Mozilla, Firefox, Thunderbird, Epiphany: New releases fix vulnerabilities |
||
|
Mozilla, Firefox, Thunderbird, Epiphany: New releases fix vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200409-26 (Mozilla, Firefox, Thunderbird, Epiphany: New releases fix vulnerabilities) Mozilla-based products are vulnerable to multiple security issues. Firstly routines handling the display of BMP images and VCards contain an integer overflow and a stack buffer overrun. Specific pages with long links, when sent using the "Send Page" function, and links with non-ASCII hostnames could both cause heap buffer overruns. Several issues were found and fixed in JavaScript rights handling: untrusted script code could read and write to the clipboard, signed scripts could build confusing grant rights dialog boxes, and when dragged onto trusted frames or windows, JavaScript links could access information and rights of the target frame or window. Finally, Mozilla-based mail clients (Mozilla and Mozilla Thunderbird) are vulnerable to a heap overflow caused by invalid POP3 mail server responses. Impact A possible hacker might be able to run arbitrary code with the rights of the user running the software by enticing the user to perform one of the following actions: view a specially-crafted BMP image or VCard, use the "Send Page" function on a malicious page, follow links with malicious hostnames, drag multiple JavaScript links in a row to another window, or connect to an untrusted POP3 mail server. A possible hacker could also use a malicious page with JavaScript to disclose clipboard contents or abuse previously-given rights to request XPI installation rights through a confusing dialog. Workaround There is no known workaround covering all vulnerabilities. References: http://www.mozilla.org/projects/security/known-vulnerabilities.html#mozilla1.7.3 http://www.us-cert.gov/cas/techalerts/TA04-261A.html Solution: All users should upgrade to the latest stable version: # emerge sync # emerge -pv your-version # emerge your-version Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

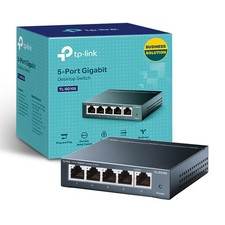
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
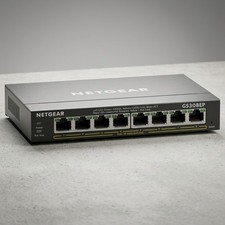
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Linksys LGS328MPC 24-Port Managed Gigabit PoE+ Switch with 4 10G SFP+ Uplinks
$224.95
|
||
|
No Discussions have been posted on this vulnerability. |