|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200409-12] ImageMagick, imlib, imlib2: BMP decoding buffer overflows Vulnerability Assessment Details
|
[GLSA-200409-12] ImageMagick, imlib, imlib2: BMP decoding buffer overflows |
||
|
ImageMagick, imlib, imlib2: BMP decoding buffer overflows Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200409-12 (ImageMagick, imlib, imlib2: BMP decoding buffer overflows) Due to improper bounds checking, ImageMagick and imlib are vulnerable to a buffer overflow when decoding runlength-encoded bitmaps. This bug can be exploited using a specially-crafted BMP image and could potentially permit remote code execution when this image is decoded by the user. Impact A specially-crafted runlength-encoded BMP could lead ImageMagick and imlib to crash or potentially execute arbitrary code. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0817 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0802 http://studio.imagemagick.org/pipermail/magick-developers/2004-August/002011.html http://securitytracker.com/alerts/2004/Aug/1011104.html http://securitytracker.com/alerts/2004/Aug/1011105.html Solution: All ImageMagick users should upgrade to the latest version: # emerge sync # emerge -pv ">=media-gfx/imagemagick-6.0.7.1" # emerge ">=media-gfx/imagemagick-6.0.7.1" All imlib users should upgrade to the latest version: # emerge sync # emerge -pv ">=media-libs/imlib-1.9.14-r2" # emerge ">=media-libs/imlib-1.9.14-r2" All imlib2 users should upgrade to the latest version: # emerge sync # emerge -pv ">=media-libs/imlib2-1.1.2" # emerge ">=media-libs/imlib2-1.1.2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

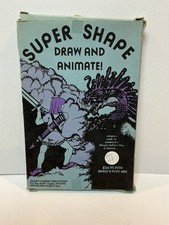
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
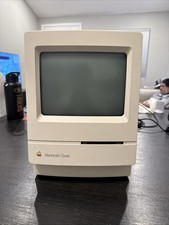
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
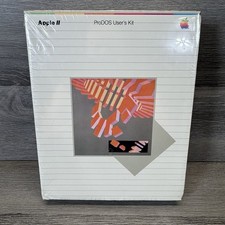
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
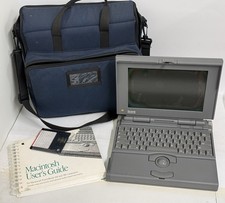
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
Vintage Apple Mac A1048 White Wired Full Size Keyboard w/ 2 USB Ports TESTED
$29.00
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |