|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200409-05] Gallery: Arbitrary command execution Vulnerability Assessment Details
|
[GLSA-200409-05] Gallery: Arbitrary command execution |
||
|
Gallery: Arbitrary command execution Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200409-05 (Gallery: Arbitrary command execution) The upload handling code in Gallery places uploaded files in a temporary directory. After 30 seconds, these files are deleted if they are not valid images. However, since the file exists for 30 seconds, a carefully crafted script could be initiated by the remote attacker during this 30 second timeout. Note that the temporary directory has to be located inside the webroot and a possible hacker needs to have upload rights either as an authenticated user or via "EVERYBODY". Impact A possible hacker could run arbitrary code as the user running PHP. Workaround There are several workarounds to this vulnerability: Make sure that your temporary directory is not contained in the webroot by default it is located outside the webroot. Disable upload rights to all albums for "EVERYBODY" upload is disabled by default. Disable debug and dev mode these settings are disabled by default. Disable permit_url_fopen in php.ini. References: http://archives.neohapsis.com/archives/fulldisclosure/2004-08/0757.html http://gallery.menalto.com/modules.php?op=modload&name=News&file=article&sid=134&mode=thread&order=0&thold=0 Solution: All Gallery users should upgrade to the latest version: # emerge sync # emerge -pv ">=www-apps/gallery-1.4.4_p2" # emerge ">=www-apps/gallery-1.4.4_p2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Samsung 32GB (2x16GB) DDR5-5600 SODIMM 32GB (2x16GB) PC5-4800 RAM Laptop
$750.00
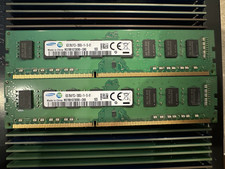
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
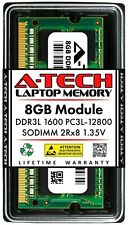
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
Crucial PC4-25600 PC4 3200AA 16GB 1X16GB DDR4 2RX8 3200MHz 260pin Memory Ram
$55.00
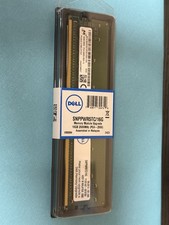
Dell 16GB PC4-21300 (DDR4-2666) Memory (SNPPWR5TC16G)
$89.99
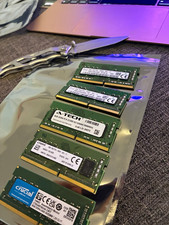
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |