|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200408-23] kdelibs: Cross-domain cookie injection vulnerability Vulnerability Assessment Details
|
[GLSA-200408-23] kdelibs: Cross-domain cookie injection vulnerability |
||
|
kdelibs: Cross-domain cookie injection vulnerability Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200408-23 (kdelibs: Cross-domain cookie injection vulnerability) kcookiejar contains a vulnerability which may permit a malicious website to set cookies for other websites under the same second-level domain. This vulnerability applies to country-specific secondary top level domains that use more than 2 characters in the secondary part of the domain name, and that use a secondary part other than com, net, mil, org, gov, edu or int. However, certain popular domains, such as co.uk, are not affected. Impact Users visiting a malicious website using the Konqueror browser may have a session cookie set for them by that site. Later, when the user visits another website under the same domain, the attacker's session cookie will be used instead of the cookie issued by the legitimate site. Depending on the design of the legitimate site, this may permit a possible hacker to gain access to the user's session. For further explanation on this type of attack, see the paper titled "Session Fixation Vulnerability in Web-based Applications" (reference 2). Workaround There is no known workaround at this time. All users are encouraged to upgrade to the latest available version of kdelibs. References: http://www.kde.org/info/security/advisory-20040823-1.txt http://www.acros.si/papers/session_fixation.pdf Solution: All kdelibs users should upgrade to the latest version: # emerge sync # emerge -pv ">=kde-base/kdelibs-3.2.3-r2" # emerge ">=kde-base/kdelibs-3.2.3-r2" Network Security Threat Level: Low Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
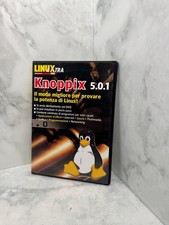
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |