|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200408-13] kdebase, kdelibs: Multiple security issues Vulnerability Assessment Details
|
[GLSA-200408-13] kdebase, kdelibs: Multiple security issues |
||
|
kdebase, kdelibs: Multiple security issues Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200408-13 (kdebase, kdelibs: Multiple security issues) KDE contains three security issues: Insecure handling of temporary files when running KDE applications outside of the KDE environment DCOPServer creates temporary files in an insecure manner The Konqueror browser permits websites to load webpages into a target frame of any other open frame-based webpage Impact A possible hacker could exploit these vulnerabilities to create or overwrite files with the permissions of another user, compromise the account of users running a KDE application and insert arbitrary frames into an otherwise trusted webpage. Workaround There is no known workaround at this time. All users are encouraged to upgrade to the latest available version of kdebase. References: http://www.kde.org/info/security/advisory-20040811-1.txt http://www.kde.org/info/security/advisory-20040811-2.txt http://www.kde.org/info/security/advisory-20040811-3.txt Solution: All KDE users should upgrade to the latest versions of kdelibs and kdebase: # emerge sync # emerge -pv ">=kde-base/kdebase-3.2.3-r1" # emerge ">=kde-base/kdebase-3.2.3-r1" # emerge -pv ">=kde-base/kdelibs-3.2.3-r1" # emerge ">=kde-base/kdelibs-3.2.3-r1" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
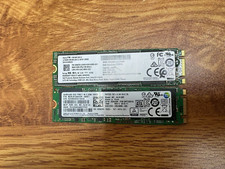
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
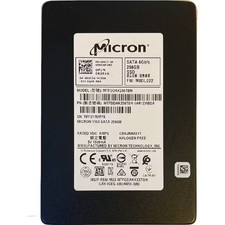
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
|
||
|
No Discussions have been posted on this vulnerability. |