|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200407-21] Samba: Multiple buffer overflows Vulnerability Assessment Details
|
[GLSA-200407-21] Samba: Multiple buffer overflows |
||
|
Samba: Multiple buffer overflows Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200407-21 (Samba: Multiple buffer overflows) Evgeny Demidov found a buffer overflow in SWAT, located in the base64 data decoder used to handle HTTP basic authentication (CVE-2004-0600). The same flaw is present in the code used to handle the sambaMungedDial attribute value, when using the ldapsam passdb backend. Another buffer overflow was found in the code used to support the 'mangling method = hash' smb.conf option (CVE-2004-0686). Note that the default Samba value for this option is 'mangling method = hash2' which is not vulnerable. Impact The SWAT authentication overflow could be exploited to execute arbitrary code with the rights of the Samba daemon process. The overflow in the sambaMungedDial handling code is not thought to be exploitable. The buffer overflow in 'mangling method = hash' code could also be used to execute arbitrary code on vulnerable configurations. Workaround Users disabling SWAT, not using ldapsam passdb backends and not using the 'mangling method = hash' option are not vulnerable. References: http://www.samba.org/samba/whatsnew/samba-3.0.5.html http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0600 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0686 Solution: All Samba users should upgrade to the latest version: # emerge sync # emerge -pv ">=net-fs/samba-3.0.5" # emerge ">=net-fs/samba-3.0.5" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$269.10
Microsoft Windows 11 Pro 64bit - New Sealed – Flash USB 1 PC
$49.99
2021 Full Version Office Professional Plus for 1 PC Flash USB Drive
$59.99
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
USB Type-A Flash Drive Metal Memory Stick High Speed USB Drive 128GB 256GB 512GB
$8.47
Lot 5/10pcs USB Flash Drive Memory Stick 1MB-64GB Pendrive Thumb Drive 8GB 32GB
$246.00
Wholesale 5/10/100PCS 1MB- 64GB USB 2.0 Flash Drive Memory Stick Jump Drive Lot
$280.00
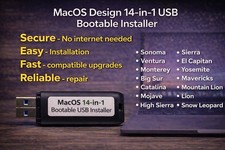
128GB USB 14-in-1 MacOS bootable Installer repair recovery tech support service
$39.99
Windows 11 Pro Install/Recovery/Repair USB Flash Drive
$35.00
|
||
|
No Discussions have been posted on this vulnerability. |