|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200407-16] Linux Kernel: Multiple DoS and permission vulnerabilities Vulnerability Assessment Details
|
[GLSA-200407-16] Linux Kernel: Multiple DoS and permission vulnerabilities |
||
|
Linux Kernel: Multiple DoS and permission vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200407-16 (Linux Kernel: Multiple DoS and permission vulnerabilities) Workaround 2.4 users may not be affected by CVE-2004-0497 if they do not use remote network filesystems and do not have support for any such filesystems in their kernel configuration. All 2.6 users are affected by the /proc attribute issue and the only known workaround is to disable /proc support. The VServer flaw applies only to vserver-sources, and no workaround is currently known for the issue. There is no known fix to CVE-2004-0447, CVE-2004-0496 or CVE-2004-0565 other than to upgrade the kernel to a patched version. As a result, all users affected by any of these vulnerabilities should upgrade their kernels to ensure the integrity of their systems. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0447 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0496 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0497 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0565 http://www.securityfocus.com/archive/1/367977 Solution: Users are encouraged to upgrade to the latest available sources for their system: # emerge sync # emerge -pv your-favorite-sources # emerge your-favorite-sources # # Follow usual procedure for compiling and installing a kernel. # # If you use genkernel, run genkernel as you would do normally. Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

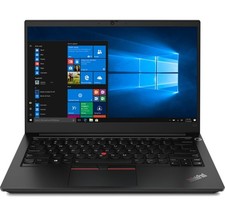
Lenovo ThinkPad E14 Gen 2 Laptop 14” HD Ryzen 5 16GB RAM 512GB SSD Win 11 Pro
$334.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
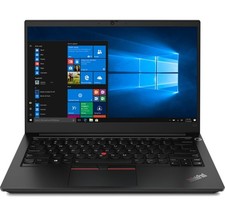
Lenovo ThinkPad E14 Gen 3 Laptop 14” FHD AMD Ryzen 5 16GB RAM 512GB SSD Win 11
$374.99
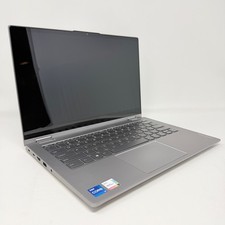
Lenovo Thinkbook 14s Yoga ITL 14” Core i7-1165G7, 16GB RAM, 512GB SSD Touch
$379.00
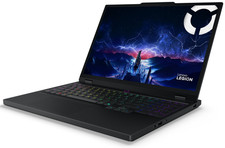
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00
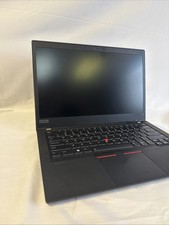
Lenovo ThinkPad T14 Gen 1 14" AMD Ryzen 5 16GB 256GB SSD
$219.99
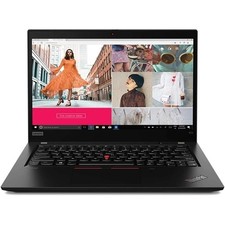
Lenovo ThinkPad X13 Gen 1 i5-10310U 16GB 512GB SSD Touch Win 11 Pro Good
$222.99
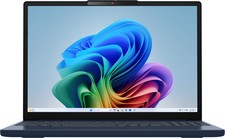
Lenovo - IdeaPad Slim 3i 15.3" 2K Touchscreen Laptop - Intel Core 7 350 2026 ...
$679.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad T495 14” Laptop AMD Ryzen 5 PRO 16GB RAM 256GB SSD Windows 11
$229.99
|
||
|
No Discussions have been posted on this vulnerability. |