|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200407-13] PHP: Multiple security vulnerabilities Vulnerability Assessment Details
|
[GLSA-200407-13] PHP: Multiple security vulnerabilities |
||
|
PHP: Multiple security vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200407-13 (PHP: Multiple security vulnerabilities) Several security vulnerabilities were found and fixed in version 4.3.8 of PHP. The strip_tags() function, used to sanitize user input, could in certain cases permit tags containing \0 characters (CVE-2004-0595). When memory_limit is used, PHP might unsafely interrupt other functions (CVE-2004-0594). The ftok and itpc functions were missing safe_mode checks. It was possible to bypass open_basedir restrictions using MySQL's LOAD DATA LOCAL function. Furthermore, the IMAP extension was incorrectly allocating memory and alloca() calls were replaced with emalloc() for better stack protection. Impact Successfully exploited, the memory_limit problem could permit remote excution of arbitrary code. By exploiting the strip_tags vulnerability, it is possible to pass HTML code that would be considered as valid tags by the Microsoft Internet Explorer and Safari browsers. Using ftok, itpc or MySQL's LOAD DATA LOCAL, it is possible to bypass PHP configuration restrictions. Workaround There is no known workaround that would solve all these problems. All users are encouraged to upgrade to the latest available versions. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0594 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0595 http://security.e-matters.de/advisories/112004.html http://security.e-matters.de/advisories/122004.html Solution: All PHP, mod_php and php-cgi users should upgrade to the latest stable version: # emerge sync # emerge -pv ">=dev-php/php-4.3.8" # emerge ">=dev-php/php-4.3.8" # emerge -pv ">=dev-php/mod_php-4.3.8" # emerge ">=dev-php/mod_php-4.3.8" # emerge -pv ">=dev-php/php-cgi-4.3.8" # emerge ">=dev-php/php-cgi-4.3.8" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
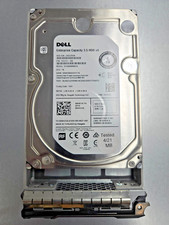
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
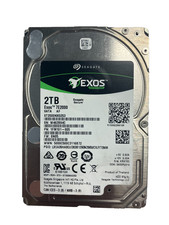
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
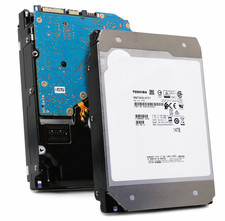
Toshiba 14TB MG07 MG07ACA14TEY 7.2K RPM SATA 6Gb/s 512e 3.5" Enterprise HDD
$339.00
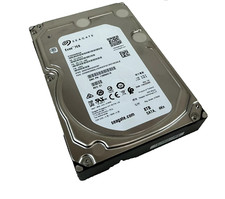
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99

Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
|
||
|
No Discussions have been posted on this vulnerability. |