|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200407-12] Linux Kernel: Remote DoS vulnerability with IPTables TCP Handling Vulnerability Assessment Details
|
[GLSA-200407-12] Linux Kernel: Remote DoS vulnerability with IPTables TCP Handling |
||
|
Linux Kernel: Remote DoS vulnerability with IPTables TCP Handling Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200407-12 (Linux Kernel: Remote DoS vulnerability with IPTables TCP Handling) A possible hacker can utilize an erroneous data type in the IPTables TCP option handling code, which lies in an iterator. By making a TCP packet with a header length larger than 127 bytes, a negative integer would be implied in the iterator. Impact By sending one malformed packet, the kernel could get stuck in a loop, consuming all of the CPU resources and rendering the machine useless, causing a Denial of Service. This vulnerability requires no local access. Workaround If users do not use the netfilter functionality or do not use any ``--tcp-option'' rules they are not vulnerable to this exploit. Users that are may remove netfilter support from their kernel or may remove any ``--tcp-option'' rules they might be using. However, all users are urged to upgrade their kernels to patched versions. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0626 Solution: Users are encouraged to upgrade to the latest available sources for their system: # emerge sync # emerge -pv your-favorite-sources # emerge your-favorite-sources # # Follow usual procedure for compiling and installing a kernel. # # If you use genkernel, run genkernel as you would do normally. Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

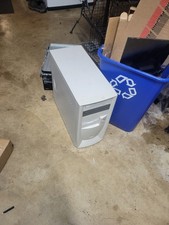
vintage pentium 3 pc turns on no display no post
$150.00
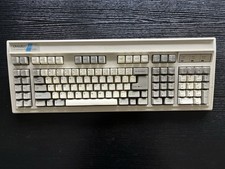
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
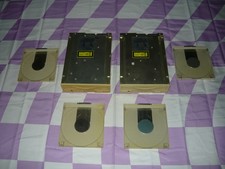
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
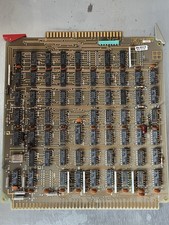
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
Vintage Avionics Gold CPU Board Intel MD8088 Ceramic LSI MCE Military Aerospace
$179.95
Vintage CREATIVE PC-DVD Dxr2 DVD2240E 1997
$59.00
Vintage Military Avionics PCB AlliedSignal 1750A CPU Ceramic Aerospace Board
$299.95
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
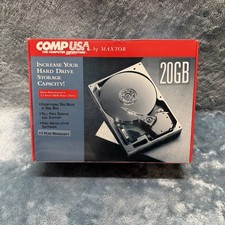
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
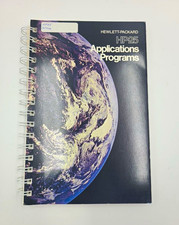
Vintage Hewlett-Packard HP-25 Applications Programs 1975 Manual 00025-90011
$29.50
|
||
|
No Discussions have been posted on this vulnerability. |