|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200407-10] rsync: Directory traversal in rsync daemon Vulnerability Assessment Details
|
[GLSA-200407-10] rsync: Directory traversal in rsync daemon |
||
|
rsync: Directory traversal in rsync daemon Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200407-10 (rsync: Directory traversal in rsync daemon) When rsyncd is used without chroot ("use chroot = false" in the rsyncd.conf file), the paths sent by the client are not checked thoroughly enough. If rsyncd is used with read-write permissions ("read only = false"), this vulnerability can be used to write files anywhere with the rights of the rsyncd daemon. With default Gentoo installations, rsyncd runs in a chroot, without write permissions and with the rights of the "nobody" user. Impact On affected configurations and if the rsync daemon runs under a privileged user, a remote client can exploit this vulnerability to completely compromise the host. Workaround You should never set the rsync daemon to run with "use chroot = false". If for some reason you have to run rsyncd without a chroot, then you should not set "read only = false". References: http://www.cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0426 Solution: All users should update to the latest version of the rsync package. # emerge sync # emerge -pv ">=net-misc/rsync-2.6.0-r2" # emerge ">=net-misc/rsync-2.6.0-r2" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
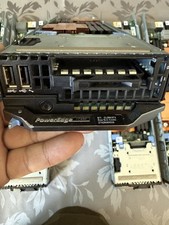
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
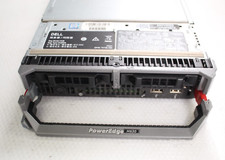
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$95.20
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
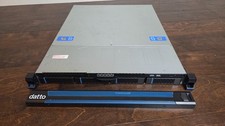
Datto S4P10 1U Blade Rack Server Intel Xeon D-2143IT 2.20GHz 48GB DDR4 4-Bay PSU
$229.95
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
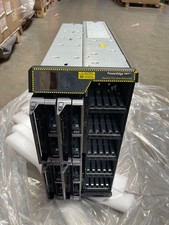
Dell PowerEdge VRTX 2.5"x25 Bay Blade Enclosure 4x1600W + 4X M640 (4X Blades)
$1599.99
Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08
|
||
|
No Discussions have been posted on this vulnerability. |