|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200406-21] mit-krb5: Multiple buffer overflows in krb5_aname_to_localname Vulnerability Assessment Details
|
[GLSA-200406-21] mit-krb5: Multiple buffer overflows in krb5_aname_to_localname |
||
|
mit-krb5: Multiple buffer overflows in krb5_aname_to_localname Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200406-21 (mit-krb5: Multiple buffer overflows in krb5_aname_to_localname) The library function krb5_aname_to_localname() contains multiple buffer overflows. This is only exploitable if explicit mapping or rules-based mapping is enabled. These are not enabled as default. With explicit mapping enabled, a possible hacker must authenticate using a principal name listed in the explicit mapping list. With rules-based mapping enabled, a possible hacker must first be able to create arbitrary principal names either in the local realm Kerberos realm or in a remote realm from which the local realm's service are reachable by cross-realm authentication. Impact A possible hacker could use these vulnerabilities to execute arbitrary code with the permissions of the user running mit-krb5, which could be the root user. Workaround There is no known workaround at this time. All users are encouraged to upgrade to the latest available version. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0523 http://web.mit.edu/kerberos/advisories/MITKRB5-SA-2004-001-an_to_ln.txt Solution: mit-krb5 users should upgrade to the latest version: # emerge sync # emerge -pv ">=app-crypt/mit-krb5-1.3.3-r1" # emerge ">=app-crypt/mit-krb5-1.3.3-r1" Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

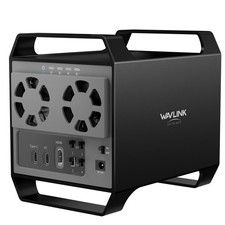
2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
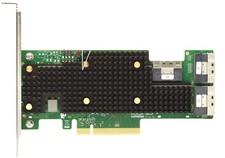
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
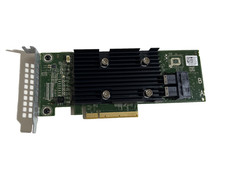
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
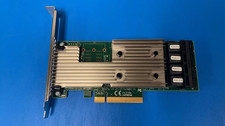
Broadcom LSI 9305-16i 12Gbps SAS-3 PCIe x8 HBA 16-Ports Raid Controller
$64.99
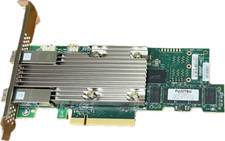
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |