|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200406-20] FreeS/WAN, Openswan, strongSwan: Vulnerabilities in certificate handling Vulnerability Assessment Details
|
[GLSA-200406-20] FreeS/WAN, Openswan, strongSwan: Vulnerabilities in certificate handling |
||
|
FreeS/WAN, Openswan, strongSwan: Vulnerabilities in certificate handling Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200406-20 (FreeS/WAN, Openswan, strongSwan: Vulnerabilities in certificate handling) All these IPsec implementations have several bugs in the verify_x509cert() function, which performs certificate validation, that make them vulnerable to malicious PKCS#7 wrapped objects. Impact With a carefully crafted certificate payload a possible hacker can successfully authenticate against FreeS/WAN, Openswan, strongSwan or Super-FreeS/WAN, or make the daemon go into an endless loop. Workaround There is no known workaround at this time. All users are encouraged to upgrade to the latest available version. References: http://lists.openswan.org/pipermail/dev/2004-June/000370.html Solution: All FreeS/WAN 1.9x users should upgrade to the latest stable version: # emerge sync # emerge -pv "=net-misc/freeswan-1.99-r1" # emerge "=net-misc/freeswan-1.99-r1" All FreeS/WAN 2.x users should upgrade to the latest stable version: # emerge sync # emerge -pv ">=net-misc/freeswan-2.04-r1" # emerge ">=net-misc/freeswan-2.04-r1" All Openswan 1.x users should upgrade to the latest stable version: # emerge sync # emerge -pv "=net-misc/openswan-1.0.6_rc1" # emerge "=net-misc/openswan-1.0.6_rc1" All Openswan 2.x users should upgrade to the latest stable version: # emerge sync # emerge -pv ">=net-misc/openswan-2.1.4" # emerge ">=net-misc/openswan-2.1.4" All strongSwan users should upgrade to the latest stable version: # emerge sync # emerge -pv ">=net-misc/strongswan-2.1.3" # emerge ">=net-misc/strongswan-2.1.3" All Super-FreeS/WAN users should migrate to the latest stable version of Openswan. Note that Portage will force a move for Super-FreeS/WAN users to Openswan. # emerge sync # emerge -pv "=net-misc/openswan-1.0.6_rc1" # emerge "=net-misc/openswan-1.0.6_rc1" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

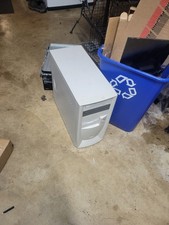
vintage pentium 3 pc turns on no display no post
$150.00
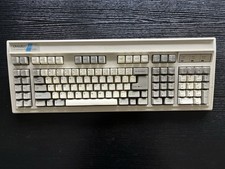
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
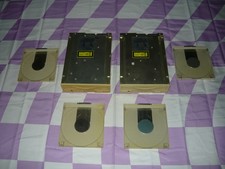
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
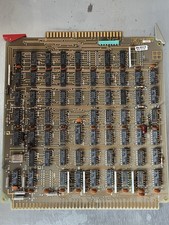
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
MicroProse Falcon 4.0 PC Flight Sim Big Box Manuals Korean Map CD Lot Vintage
$60.00
Vintage Military Avionics PCB AlliedSignal 1750A CPU Ceramic Aerospace Board
$299.95
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
Vintage Military Avionics PCB Philips Ceramic ASIC Gold Lid Aerospace Computer
$99.95
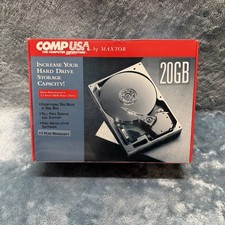
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
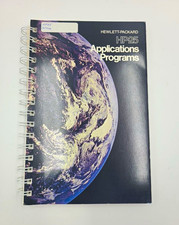
Vintage Hewlett-Packard HP-25 Applications Programs 1975 Manual 00025-90011
$29.50
|
||
|
No Discussions have been posted on this vulnerability. |