|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200405-22] Apache 1.3: Multiple vulnerabilities Vulnerability Assessment Details
|
[GLSA-200405-22] Apache 1.3: Multiple vulnerabilities |
||
|
Apache 1.3: Multiple vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200405-22 (Apache 1.3: Multiple vulnerabilities) On 64-bit big-endian platforms, mod_access does not properly parse Allow/Deny rules using IP addresses without a netmask which could result in failure to match certain IP addresses. Terminal escape sequences are not filtered from error logs. This could be used by a possible hacker to insert escape sequences into a terminal emulater vulnerable to escape sequences. mod_digest does not properly verify the nonce of a client response by using a AuthNonce secret. This could permit a possible hacker to replay the response of another website. This does not affect mod_auth_digest. On certain platforms there is a starvation issue where listening sockets fails to handle short-lived connection on a rarely-accessed listening socket. This causes the child to hold the accept mutex and block out new connections until another connection arrives on the same rarely-accessed listening socket thus leading to a denial of service. Impact These vulnerabilities could lead to attackers bypassing intended access restrictions, denial of service, and possibly execution of arbitrary code. Workaround There is no known workaround at this time. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2003-0993 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2003-0020 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2003-0987 http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0174 Solution: All users should upgrade to the latest stable version of Apache 1.3. # emerge sync # emerge -pv ">=net-www/apache-1.3.31" # emerge ">=net-www/apache-1.3.31" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

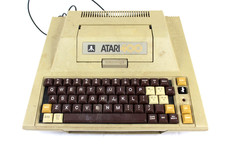
VTG Atari 400 Home Computer System ** Sold "AS-IS" for Parts or Repair
$88.75
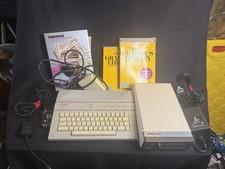
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
DEFECTIVE Atari 810 Vintage Computer Disk Drive powers on Unit Only Boo G3D
$49.29
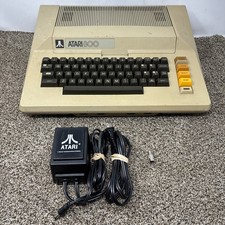
Atari 800 8-bit Computer System Fully Tested Great Condition 48k READ
$350.00
Atari 1050 Floppy Disk Drive with Power Supply, MPN C061636 (Vintage)
$80.00
Atari XE 130XE Computer NTSC with Power Supply Powers On Untested
$159.95
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
SDrive Max Floppy Drive Emulator Atari 8-Bit 400/800/XL/XE Firmware 1.5 USB C R2
$70.00
UNOCART-2600 SD card Multi Rom Cartridge for ATARI 2600 with CASE
$34.25
Vintage Atari SF354 Floppy Disk Drive & Power Supply FOR PARTS OR REPAIR AS IS
$120.00
|
||
|
No Discussions have been posted on this vulnerability. |