|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200405-19] Opera telnet URI handler file creation/truncation vulnerability Vulnerability Assessment Details
|
[GLSA-200405-19] Opera telnet URI handler file creation/truncation vulnerability |
||
|
Opera telnet URI handler file creation/truncation vulnerability Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200405-19 (Opera telnet URI handler file creation/truncation vulnerability) The telnet URI handler in Opera does not check for leading '-' characters in the host name. Consequently, a maliciously-crafted telnet:// link may be able to pass options to the telnet program itself. One example would be the following: telnet://-nMyFile If MyFile exists in the user's home directory and the user clicking on the link has write permissions to it, the contents of the file will be overwritten with the output of the telnet trace information. If MyFile does not exist, the file will be created in the user's home directory. Impact This exploit has two possible impacts. First, it may create new files in the user's home directory. Second, and far more serious, it may overwrite existing files that the user has write permissions to. A possible hacker with some knowledge of a user's home directory might be able to destroy important files stored within. Workaround Disable the telnet URI handler from within Opera. References: http://www.idefense.com/application/poi/display?id=104&type=vulnerabilities&flashstatus=true Solution: All Opera users are encouraged to upgrade to the latest version of the program: # emerge sync # emerge -pv ">=net-www/opera-7.50_beta1" # emerge ">=net-www/opera-7.50_beta1" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

OEM Genuine 42Wh WDX0R For DELL Inspiron WDXOR Battery 15 5567 5568 13 5368 7368
$22.99
OEM 68Wh 3HWPP Battery For Dell Latitude 5401 5501 5410 5510 E5411 E5511
$28.99
Genuine OEM 6GTPY 97Wh Battery for Dell XPS 15 7590, 9550 Series 5XJ28 GPM03 New
$33.50
OEM Genuine 95WH PKWVM C903V Battery 7550 For Dell Precision CR72X 17C06 447VR
$37.40
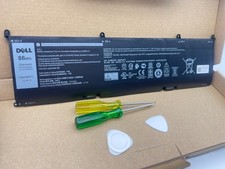
OEM Genuine 86WH 69KF2 Battery For Dell XPS 15 9500 Precision 5550 M59JH M15 M17
$45.49
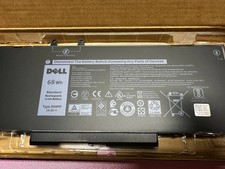
OEM 68Wh 3HWPP Battery For Dell Latitude 5401 5411 15 5501 5511 Precision 3541
$35.78
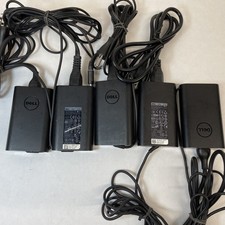
Lot of 5 Dell OEM 65W 7.4mm 19.5V 3.34A AC Adapters Mixed Models B Grade
$36.99
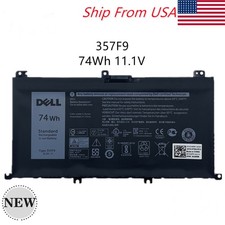
OEM 74WH 357F9 Battery For Dell Inspiron 15 7559 i7559 7557 i7557 5577 7567 5576
$26.99
Genuine OEM 63Wh 7FMXV Battery For Dell Latitude 5320 7320 7420 7520 4M1JN TN2GY
$32.99
New Genuine OEM Dell Latitude 5420 5520 3560 4 Cell Laptop Battery RJ40G M033W
$49.95
|
||
|
No Discussions have been posted on this vulnerability. |