|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200405-11] KDE URI Handler Vulnerabilities Vulnerability Assessment Details
|
[GLSA-200405-11] KDE URI Handler Vulnerabilities |
||
|
KDE URI Handler Vulnerabilities Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200405-11 (KDE URI Handler Vulnerabilities) The telnet, rlogin, ssh and mailto URI handlers in KDE do not check for '-' at the beginning of the hostname passed. By crafting a malicious URI and entice an user to click on it, it is possible to pass an option to the programs started by the handlers (typically telnet, kmail...). Impact If the attacker controls the options passed to the URI handling programs, it becomes possible for example to overwrite arbitrary files (possibly leading to denial of service), to open kmail on a possible hacker-controlled remote display or with an alternate configuration file (possibly leading to control of the user account). Workaround There is no known workaround at this time. All users are advised to upgrade to a corrected version of kdelibs. References: http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2004-0411 Solution: Users of KDE 3.1 should upgrade to the corrected version of kdelibs: # emerge sync # emerge -pv "=kde-base/kdelibs-3.1.5-r1" # emerge "=kde-base/kdelibs-3.1.5-r1" Users of KDE 3.2 should upgrade to the latest available version of kdelibs: # emerge sync # emerge -pv ">=kde-base/kdelibs-3.2.2-r1" # emerge ">=kde-base/kdelibs-3.2.2-r1" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

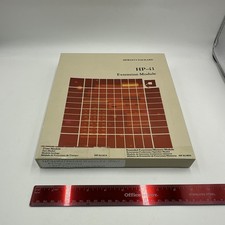
Vintage HP-41 Extension Module Box Set - HP 82182A Time Module Complete Lot
$185.00
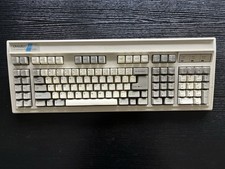
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
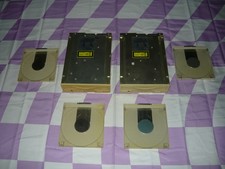
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
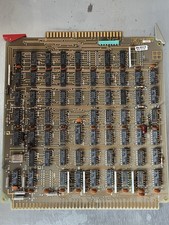
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
RARE Vintage Chicony KB-5181 Mechanical Keyboard Monterey Blue SMK Switches
$65.00
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
Vintage Magnetic Peripherals MPI BR8B1A 5.25" Floppy Disk Drive 77711800 CDC
$89.66
|
||
|
No Discussions have been posted on this vulnerability. |