|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200404-20] Multiple vulnerabilities in xine Vulnerability Assessment Details
|
[GLSA-200404-20] Multiple vulnerabilities in xine |
||
|
Multiple vulnerabilities in xine Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200404-20 (Multiple vulnerabilities in xine) Several vulnerabilities were found in xine-ui and xine-lib. By opening a malicious MRL in any xine-lib based media player, a possible hacker can write arbitrary content to an arbitrary file, only restricted by the permissions of the user running the application. By opening a malicious playlist in the xine-ui media player, a possible hacker can write arbitrary content to an arbitrary file, only restricted by the permissions of the user running xine-ui. Finally, a temporary file is created in an insecure manner by the xine-check and xine-bugreport scripts, potentially permiting a local attacker to use a symlink attack. Impact These three vulnerabilities may alow a possible hacker to corrupt system files, thus potentially leading to a Denial of Service. It is also theoretically possible, though very unlikely, to use these vulnerabilities to elevate the rights of the attacker. Workaround There is no known workaround at this time. All users are advised to upgrade to the latest available versions of xine-ui and xine-lib. References: http://xinehq.de/index.php/security http://nettwerked.mg2.org/advisories/xinebug Solution: All users of xine-ui or another xine-based player should upgrade to the latest stable versions: # emerge sync # emerge -pv ">=media-video/xine-ui-0.9.23-r2" # emerge ">=media-video/xine-ui-0.9.23-r2" # emerge -pv ">=media-libs/xine-lib-1_rc3-r3" # emerge ">=media-libs/xine-lib-1_rc3-r3" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
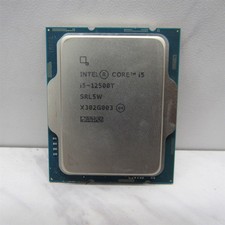
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
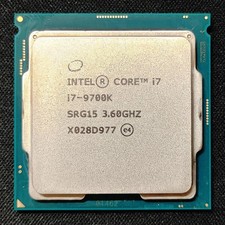
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
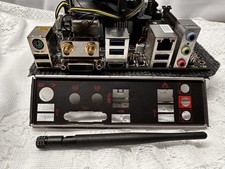
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
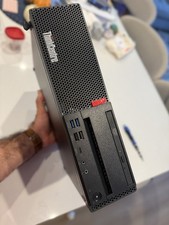
Lenovo ThinkCentre M920s SFF Barebones PC Motherboard PSU DVD No CPU RAM SSD
$27.99
|
||
|
No Discussions have been posted on this vulnerability. |