|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Gentoo Local Security Checks >> [GLSA-200401-04] GAIM 0.75 Remote overflows Vulnerability Assessment Details
|
[GLSA-200401-04] GAIM 0.75 Remote overflows |
||
|
GAIM 0.75 Remote overflows Detailed Explanation for this Vulnerability Assessment The remote host is affected by the vulnerability described in GLSA-200401-04 (GAIM 0.75 Remote overflows) Yahoo changed the authentication methods to their IM servers, rendering GAIM useless. The GAIM team released a rushed release solving this issue, however, at the same time a code audit revealed 12 new vulnerabilities. Impact Due to the nature of instant messaging many of these bugs require man-in-the-middle attacks between the client and the server. But the underlying protocols are easy to implement and attacking ordinary TCP sessions is a fairly simple task. As a result, all users are advised to upgrade their GAIM installation. Users of GAIM 0.74 or below are affected by 7 of the vulnerabilities and are encouraged to upgrade. Users of GAIM 0.75 are affected by 11 of the vulnerabilities and are encouraged to upgrade to the patched version of GAIM offered by Gentoo. Users of GAIM 0.75-r6 are only affected by 4 of the vulnerabilities, but are still urged to upgrade to maintain security. Workaround There is no immediate workaround a software upgrade is required. References: http://www.securityfocus.com/archive/1/351235/2004-01-23/2004-01-29/0 Solution: All users are recommended to upgrade GAIM to 0.75-r7. $> emerge sync $> emerge -pv ">=net-im/gaim-0.75-r7" $> emerge ">=net-im/gaim-0.75-r7" Network Security Threat Level: Medium Networks Security ID: Vulnerability Assessment Copyright: (C) 2005 Michel Arboi |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
Dell Latitude 14" Laptop Computer Intel i5 Up To 32GB RAM 1TB SSD Windows 11 Pro
$316.61

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Dell Latitude 14" Laptop Computer Intel i7 Up To 32GB RAM 1TB SSD Windows 11 Pro
$349.48
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00
1TB Kingston DataTraveler Max DTMAX/1TB USB Type-C Flash Drive
$86.95
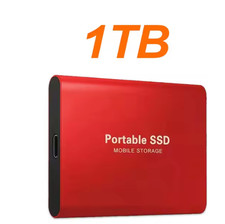
External SSD 1TB 2TB 4TB Portable Hard Drive USB 3.0 Type-C High Speed PC Mac
$19.99
Acer Predator Helios Neo 16S AI 16" i9 275HX 2S RTX 5070 Ti 32GB 1TB SSD Refurb
$1746.47
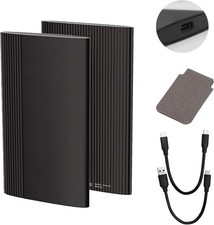
External Solid State Drive USB 3.2 Gen2, 1TB SSD External Hard Drive with C to A
$100.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
|
||
|
No Discussions have been posted on this vulnerability. |