|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 5 2006-837: sendmail Vulnerability Assessment Details
|
Fedora Core 5 2006-837: sendmail |
||
|
Check for the version of the sendmail package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2006-837 (sendmail). The Sendmail program is a very widely used Mail Transport Agent (MTA). MTAs send mail from one machine to another. Sendmail is not a client program, which you use to read your email. Sendmail is a behind-the-scenes program which actually moves your email over networks or the Internet to where you want it to go. If you ever need to reconfigure Sendmail, you will also need to have the sendmail.cf package installed. If you need documentation on Sendmail, you can install the sendmail-doc package. Update information : * Tue Jul 18 2006 Thomas Woerner - using new syntax for access database (#177566) - fixed failure message while shutting down sm-client (#119429) resolution: stop sm-client before sendmail - fixed method to specify persistent queue runners (#126760) - removed patch backup files from sendmail-cf tree (#152955) - fixed missing dnl on SMART_HOST define (#166680) - fixed wrong location of aliases and aliases.db file in aliases man page (#166744) - enabled CipherList config option for sendmail (#172352) - added user chowns for /etc/mail/authinfo.db and move check for cf files (#184341) - fixed Makefile of vacation (#191396) vacation is not included in this sendmail package - /var/log/mail now belongs to sendmail (#192850) Solution : Get the newest Fedora Updates Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

RAM-HOL-SAM60CPU RAM USB-C Powered Dock for Samsung Tab Active5 - 3 - 2
$81.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Samsung Galaxy Tab A9+ Plus 11” 128GB Android Tablet Graphite BRAND NEW SEALED.
$214.99
Samsung Galaxy View Tablet 18.4 SM-T670/677A Charging Port 100% Original Oem
$98.99
RAM-GDS-SKIN-SAM54-NG-1 RAM Mounts IntelliSkin® Next Gen for Samsung Tab Active4
$93.99
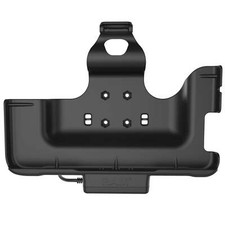
RAM-HOL-SAM52CPU RAM USB-C Powered Dock Samsung Tab Active4 Pro & Tab Active Pro
$81.99
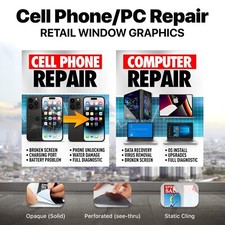
Cell Phone Smartphone Computer repair banner poster sign iphone Samsung
$89.99
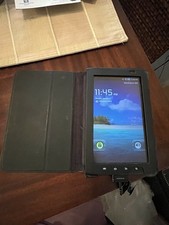
Samsung Galaxy Tab SCH-1800 7" 4GB Wi-Fi + Verizon Tablet Working
$30.00
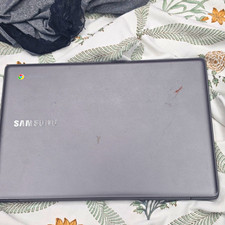
Samsung Chromebook 11.6" Intel Celeron Chrome OS Gray (Charger Inc)
$22.00
NEW Samsung NoteBook NT930QCG touch LCD Full Screen Assembly Blue
$225.77
|
||
|
No Discussions have been posted on this vulnerability. |