|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 4 2006-836: sendmail Vulnerability Assessment Details
|
Fedora Core 4 2006-836: sendmail |
||
|
Check for the version of the sendmail package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2006-836 (sendmail). The Sendmail program is a very widely used Mail Transport Agent (MTA). MTAs send mail from one machine to another. Sendmail is not a client program, which you use to read your email. Sendmail is a behind-the-scenes program which actually moves your email over networks or the Internet to where you want it to go. If you ever need to reconfigure Sendmail, you will also need to have the sendmail.cf package installed. If you need documentation on Sendmail, you can install the sendmail-doc package. Update information : * Tue Jul 18 2006 Thomas Woerner - using new syntax for access database (#177566) - fixed failure message while shutting down sm-client (#119429) resolution: stop sm-client before sendmail - fixed method to specify persistent queue runners (#126760) - removed patch backup files from sendmail-cf tree (#152955) - fixed missing dnl on SMART_HOST define (#166680) - fixed wrong location of aliases and aliases.db file in aliases man page (#166744) - enabled CipherList config option for sendmail (#172352) - added user chowns for /etc/mail/authinfo.db and move check for cf files (#184341) - fixed Makefile of vacation (#191396) vacation is not included in this sendmail package - /var/log/mail now belongs to sendmail (#192850) - using old pam_stack Solution : Get the newest Fedora Updates Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

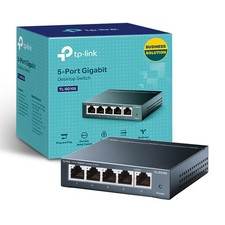
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
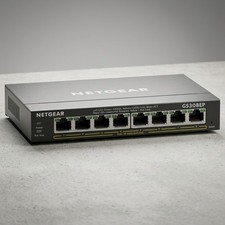
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
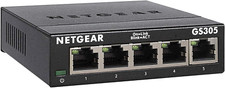
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
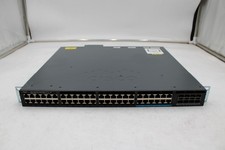
Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |