|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 4 2006-579: postgresql Vulnerability Assessment Details
|
Fedora Core 4 2006-579: postgresql |
||
|
Check for the version of the postgresql package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2006-579 (postgresql). PostgreSQL is an advanced Object-Relational database management system (DBMS) that supports almost all SQL constructs (including transactions, subselects and user-defined types and functions). The postgresql package includes the client programs and libraries that you'll need to access a PostgreSQL DBMS server. These PostgreSQL client programs are programs that directly manipulate the internal structure of PostgreSQL databases on a PostgreSQL server. These client programs can be located on the same machine with the PostgreSQL server, or may be on a remote machine which accesses a PostgreSQL server over a network connection. This package contains the docs in HTML for the whole package, as well as command-line utilities for managing PostgreSQL databases on a PostgreSQL server. If you want to manipulate a PostgreSQL database on a remote PostgreSQL server, you need this package. You also need to install this package if you're installing the postgresql-server package. Update information : * Mon May 22 2006 Tom Lane - Update to PostgreSQL 8.0.8 (includes fixes for CVE-2006-2313, CVE-2006-2314 see bug #192173) - Update to jdbc driver build 316 - Suppress noise from chcon, per bug #187744 - Repair extraneous quote in pgtcl configure script ... odd that bash didn't use to spit up on this. Solution : Get the newest Fedora Updates Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2007 Tenable Network Security |
||
|
Cables, Connectors |

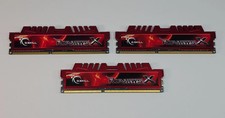
16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
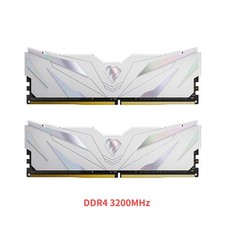
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
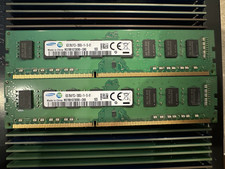
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
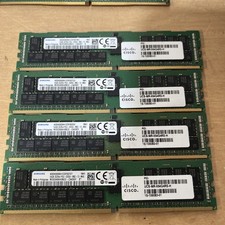
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot 500 SK hynix 16GB 2Rx8 PC4-23400 DDR4-2933Y ECC Registered Server Memory RAM
$47988.00
Corsair Vengeance DDR3 8GB 16GB 32GB 1866MHz PC3-14900 Desktop RAM Memory DIMM
$85.00
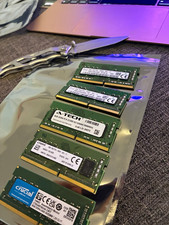
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |