|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 4 2006-052: httpd Vulnerability Assessment Details
|
Fedora Core 4 2006-052: httpd |
||
|
Check for the version of the httpd package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2006-052 (httpd). The Apache HTTP Server is a powerful, full-featured, efficient, and freely-available Web server. The Apache HTTP Server is also the most popular Web server on the Internet. Update Information: This update includes fixes for three security issues in the Apache HTTP Server. A memory leak in the worker MPM could permit remote attackers to cause a denial of service (memory consumption) via aborted connections, which prevents the memory for the transaction pool from being reused for other connections. The Common Vulnerabilities and Exposures project assigned the name CVE-2005-2970 to this issue. This vulnerability only affects users who are using the non-default worker MPM. A flaw in mod_imap when using the Referer directive with image maps was discovered. With certain site configurations, a remote attacker could perform a cross-site scripting attack if a victim can be forced to visit a malicious URL using certain web browsers. (CVE-2005-3352) A NULL pointer dereference flaw in mod_ssl was discovered affecting server configurations where an SSL virtual host is configured with access control and a custom 400 error document. A remote attacker could send a carefully crafted request to trigger this issue which would lead to a crash. This crash would only be a denial of service if using the non-default worker MPM. (CVE-2005-3357) Solution : Get the newest Fedora Updates Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Lenovo ThinkPad E14 Gen 2 Laptop 14” HD Ryzen 5 16GB RAM 512GB SSD Win 11 Pro
$334.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad E14 Gen 3 Laptop 14” FHD AMD Ryzen 5 16GB RAM 512GB SSD Win 11
$374.99
Lenovo Thinkbook 14s Yoga ITL 14” Core i7-1165G7, 16GB RAM, 512GB SSD Touch
$379.00
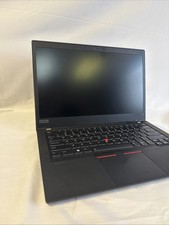
Lenovo ThinkPad T14 Gen 1 14" AMD Ryzen 5 16GB 256GB SSD
$219.99
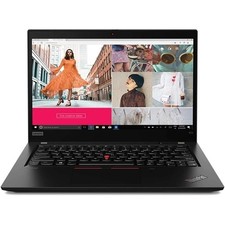
Lenovo ThinkPad X13 Gen 1 i5-10310U 16GB 512GB SSD Touch Win 11 Pro Good
$222.99
Lenovo - IdeaPad Slim 3i 15.3" 2K Touchscreen Laptop - Intel Core 7 350 2026 ...
$679.99
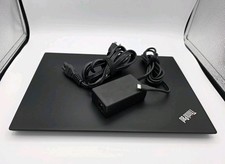
Lenovo ThinkPad T480s | i5-8350U | 256GB NVMe | 8GB RAM | W11 Pro | W/AC Adapter
$169.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo Thinkpad T14 Gen 1 14.0" 16GB 512GB, BLACK
$285.99
|
||
|
No Discussions have been posted on this vulnerability. |