|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 4 2005-553: krb5 Vulnerability Assessment Details
|
Fedora Core 4 2005-553: krb5 |
||
|
Check for the version of the krb5 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-553 (krb5). Kerberos V5 is a trusted-third-party network authentication system, which can improve your network's security by eliminating the insecure practice of cleartext passwords. Update Information: A double-free flaw was found in the krb5_recvauth() routine which may be triggered by a remote unauthenticated attacker. Fedora Core 4 contains checks within glibc that detect double-free flaws. Therefore, on Fedora Core 4, successful exploitation of this issue can only lead to a denial of service (KDC crash). The Common Vulnerabilities and Exposures project assigned the name CVE-2005-1689 to this issue. Daniel Wachdorf discovered a single byte heap overflow in the krb5_unparse_name() function, part of krb5-libs. Successful exploitation of this flaw would lead to a denial of service (crash). To trigger this flaw remotely, a possible hacker would need to have control of a kerberos realm that shares a cross-realm key with the target, making exploitation of this flaw unlikely. (CVE-2005-1175). Daniel Wachdorf also discovered that in error conditions that may occur in response to correctly-formatted client requests, the Kerberos 5 KDC may attempt to free uninitialized memory. This could permit a remote attacker to cause a denial of service (KDC crash) (CVE-2005-1174). Ga�l Delalleau discovered an information disclosure issue in the way some telnet clients handle messages from a server. A possible hacker could construct a malicious telnet server that collects information from the environment of any victim who connects to it using the Kerberos-aware telnet client (CVE-2005-0488). The rcp protocol permits a server to instruct a client to write to arbitrary files outside of the current directory. This could potentially cause a security issue if a user uses the Kerberos-aware rcp to copy files from a malicious server (CVE-2004-0175). Solution : http://fedoranews.org//mediawiki/index.php/Fedora_Core_4_Update:_krb5-1.4.1-5 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

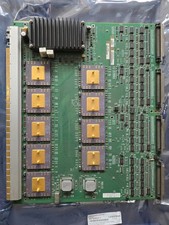
Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$729.99
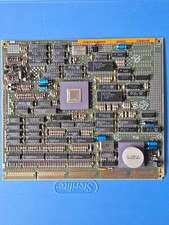
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$109.99
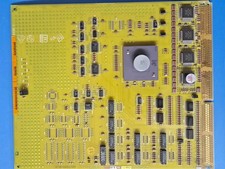
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
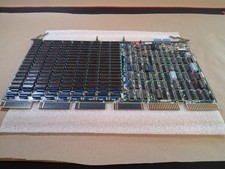
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
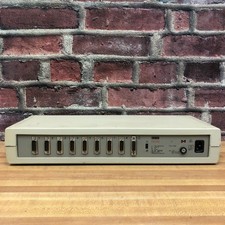
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
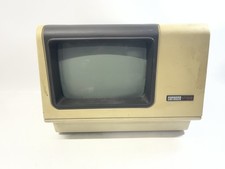
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
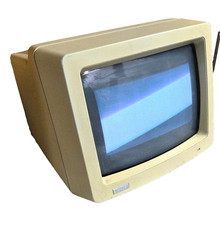
Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
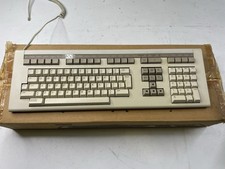
Vintage DEC LK201 Digital Equipment Corporation (DEC) LK201-AA Computer Keyboard
$149.99
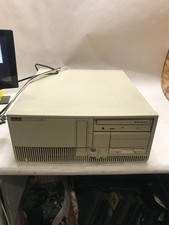
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
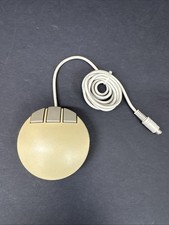
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00
|
||
|
No Discussions have been posted on this vulnerability. |