|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 4 2005-1066: spamassassin Vulnerability Assessment Details
|
Fedora Core 4 2005-1066: spamassassin |
||
|
Check for the version of the spamassassin package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-1066 (spamassassin). SpamAssassin provides you with a way to reduce if not completely eliminate Unsolicited Commercial Email (SPAM) from your incoming email. It can be invoked by a MDA such as sendmail or postfix, or can be called from a procmail script, .forward file, etc. It uses a genetic-algorithm evolved scoring system to identify messages which look spammy, then adds headers to the message so they can be filtered by the user's mail reading software. This distribution includes the spamd/spamc components which create a server that considerably speeds processing of mail. To enable spamassassin, if you are receiving mail locally, simply add this line to your ~/.procmailrc: INCLUDERC=/etc/mail/spamassassin/spamassassin-default.rc To filter spam for all users, add that line to /etc/procmailrc (creating if necessary). Update Information: Solves CVE-2005-3351 and a few other minor bugs to improve spam detection accuracy. You could consider this a release candidate for 3.0.5. Also solved is #161785 which ensures that 'service spamassassin restart' should never fail. Solution : Get the newest Fedora Updates Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
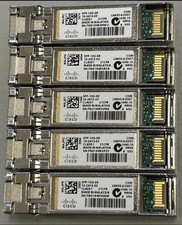
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
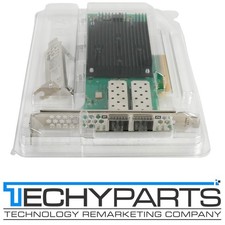
SolarFlare XtremeScale X2522-25G-PLUS Dual Port 25G SFP28 PCI-E 3.1 x8 NIC FH LP
$899.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |