|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 3 2005-392: kernel Vulnerability Assessment Details
|
Fedora Core 3 2005-392: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-392 (kernel). The kernel package contains the Linux kernel (vmlinuz), the core of any Linux operating system. The kernel handles the basic functions of the operating system: memory allocation, process allocation, device input and output, etc. * Tue May 17 2005 Dave Jones - Remove the unused (and outdated) Xen patches from the FC3 tree. * Mon May 16 2005 Dave Jones - Rebase to 2.6.11.10, (fixing CVE-2005-1264) * Thu May 12 2005 Dave Jones - Rebase to 2.6.11.9, (fixing CVE-2005-1263) * Tue May 10 2005 Dave Jones - Fix two bugs in x86-64 page fault handler. * Mon May 9 2005 Dave Jones - Rebase to 2.6.11.8 | Fixes CVE-2005-1368 (local DoS in key lookup). (#156680) | Fixes CVE-2005-1369 (i2c alarms sysfs DoS). (#156683) - Merge IDE fixes from 2.6.11-ac7 - Add Conflicts for older IPW firmwares. - Fix conntrack leak with raw sockets. * Sun May 1 2005 Dave Jones - Various firewire fixes backported from -mm. (#133798) (Thanks to Jody McIntyre for doing this) * Fri Apr 29 2005 Dave Jones - fix oops in aacraid open when using adaptec tools. (#148761) - Blacklist another brainless SCSI scanner. (#155457) * Thu Apr 21 2005 Dave Jones - Fix up SCSI queue locking. (#155472) * Tue Apr 19 2005 Dave Jones - SCSI tape security: require CAP_ADMIN for SG_IO etc. (#155355) * Mon Apr 18 2005 Dave Jones - Retry more aggressively during USB device initialization * Thu Apr 14 2005 Dave Jones - Build DRM modular. (#154769) * Fri Apr 8 2005 Dave Jones - Disable Longhaul driver (again). Solution : http://www.fedoranews.org/blog/index.php?p=695 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

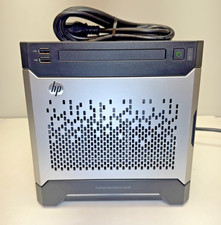
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
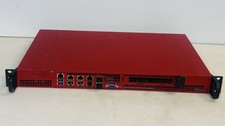
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
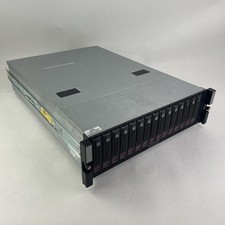
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
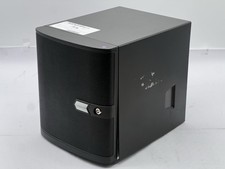
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
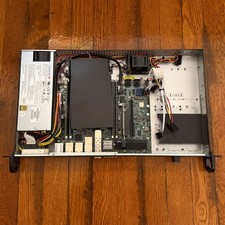
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |