|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 3 2005-106: squid Vulnerability Assessment Details
|
Fedora Core 3 2005-106: squid |
||
|
Check for the version of the squid package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-106 (squid). Squid is a high-performance proxy caching server for Web clients, supporting FTP, gopher, and HTTP data objects. Unlike traditional caching software, Squid handles all requests in a single, non-blocking, I/O-driven process. Squid keeps meta data and especially hot objects cached in RAM, caches DNS lookups, supports non-blocking DNS lookups, and implements negative caching of failed requests. Squid consists of a main server program squid, a Domain Name System lookup program (dnsserver), a program for retrieving FTP data (ftpget), and some management and client tools. * Tue Feb 01 2005 Jay Fenlason 7:2.5.STABLE7-1.FC3.1 - Add more upstream patches, including fixes for bz#146783 Correct handling of oversized reply headers bz#146778 CVE-2005-0211 Buffer overflow in WCCP recvfrom() call * Thu Jan 20 2005 Jay Fenlason 7:2.5.STABLE7-1.FC3 - Upgrade to 2.5.STABLE7 and 18 upstream patches. - This includes fixes for CVE-2005-0094 CVE-2005-0095 CVE-2004-0096 and CVE-2004-0097. This closes bz#145543 and bz#141938 - This obsoletes Ulrich Drepper's -nonbl patch. - Add a triggerin on samba-common to make /var/cache/samba/winbindd_privileged accessable so that ntlm_auth will work. This fixes bz#103726 Solution : http://www.fedoranews.org/blog/index.php?p=357 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

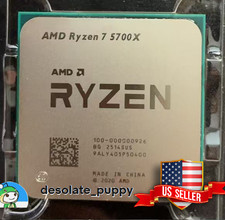
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
Lenovo IdeaPad S340-15IWL Laptop 15.6" Intel Core i3-8145U 8GB RAM 256GB SSD
$126.65
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 7800X3D 4.20GHz Quad Core 100-000000510 8 Thread AM4
$279.99
AMD Ryzen 7 5700G 8-Core 16-Thread 4.6GHz Max Boost, 3.8 GHz Base
$170.00
$600.00
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |