|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 3 2005-001: exim Vulnerability Assessment Details
|
Fedora Core 3 2005-001: exim |
||
|
Check for the version of the exim package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2005-001 (exim). Exim is a mail transport agent (MTA) developed at the University of Cambridge for use on Unix systems connected to the Internet. In style it is similar to Smail 3, but its facilities are more extensive, and in particular it has options for verifying incoming sender and recipient addresses, for refusing mail from specified hosts, networks, or senders, and for controlling mail relaying. Exim is in production use at quite a few sites, some of which move hundreds of thousands of messages per day. Exiscan is compiled in to permit inbuilt scanning capability. See http://duncanthrax.net/exiscan-acl/ Update Information: This erratum fixes two relatively minor security issues which were discovered in Exim in the last few weeks. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2005-0021 and CVE-2005-0022 to these, respectively. 1. The function host_aton() can overflow a buffer if it is presented with an illegal IPv6 address that has more than 8 components. 2. The second report described a buffer overflow in the function spa_base64_to_bits(), which is part of the code for SPA authentication. This code originated in the Samba project. The overflow can be exploited only if you are using SPA authentication. Solution : http://www.fedoranews.org/blog/index.php?p=252 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

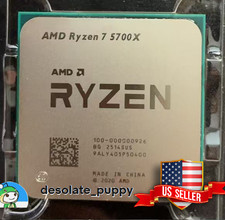
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
Lenovo IdeaPad S340-15IWL Laptop 15.6" Intel Core i3-8145U 8GB RAM 256GB SSD
$126.65
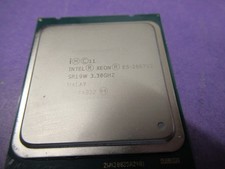
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 7800X3D 4.20GHz Quad Core 100-000000510 8 Thread AM4
$279.99
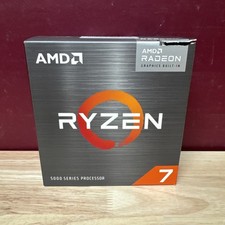
AMD Ryzen 7 5700G 8-Core 16-Thread 4.6GHz Max Boost, 3.8 GHz Base
$170.00
$600.00
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |