|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 2 2004-584: tetex Vulnerability Assessment Details
|
Fedora Core 2 2004-584: tetex |
||
|
Check for the version of the tetex package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-584 (tetex). TeTeX is an implementation of TeX for Linux or UNIX systems. TeX takes a text file and a set of formatting commands as input and creates a typesetter-independent .dvi (DeVice Independent) file as output. Usually, TeX is used in conjunction with a higher level formatting package like LaTeX or PlainTeX, since TeX by itself is not very user-friendly. Install tetex if you want to use the TeX text formatting system. If you are installing tetex, you will also need to install tetex-afm (a PostScript(TM) font converter for TeX), tetex-dvips (for converting .dvi files to PostScript format for printing on PostScript printers), tetex-latex (a higher level formatting package which provides an easier-to-use interface for TeX), and tetex-xdvi (for previewing .dvi files in X). Unless you are an expert at using TeX, you should also install the tetex-doc package, which includes the documentation for TeX. Update Information: The updated tetex package fixes a buffer overflow which permits attackers to cause the internal xpdf library used by applications in tetex to crash, and possibly to execute arbitrary code. The Common Vulnerabilities and Exposures projects (cve.mitre.org) has assigned the name CVE-2004-1125 to this issue. Solution : http://www.fedoranews.org/blog/index.php?p=234 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

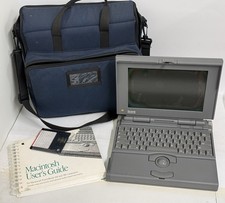
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
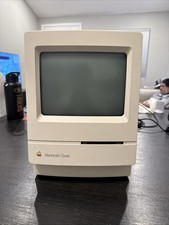
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
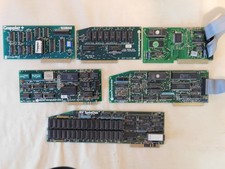
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
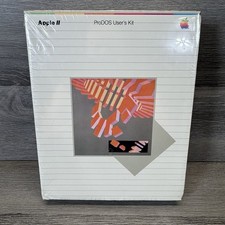
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
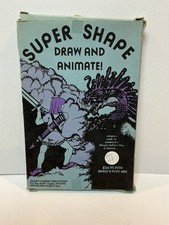
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
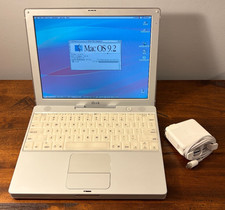
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
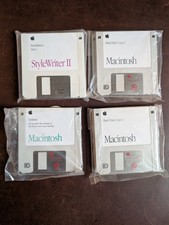
Vintage 1992 Mac System 7.1P1 Apple Software 3.5” Floppy Disks NOS
$35.00
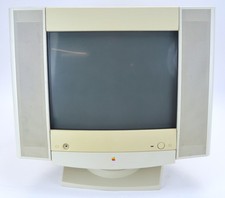
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
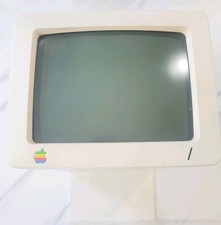
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |