|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 2 2004-295: lha Vulnerability Assessment Details
|
Fedora Core 2 2004-295: lha |
||
|
Check for the version of the lha package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-295 (lha). LHA is an archiving and compression utility for LHarc format archives. LHA is mostly used in the DOS world, but can be used under Linux to extract DOS files from LHA archives. Install the lha package if you need to extract DOS files from LHA archives. Update Information: Lukasz Wojtow discovered a stack-based buffer overflow in all versions of lha up to and including version 1.14. A carefully created archive could permit a possible hacker to execute arbitrary code when a victim extracts or tests the archive. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0769 to this issue. Buffer overflows were discovered in the command line processing of all versions of lha up to and including version 1.14. If a malicious user can trick a victim into passing a specially crafted command line to the lha command, it is possible that arbitrary code could be executed. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2004-0771 and CVE-2004-0694 to these issues. Thomas Biege discovered a shell meta character command execution vulnerability in all versions of lha up to and including 1.14. A possible hacker could create a directory with shell meta characters in its name which could lead to arbitrary command execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0745 to this issue. Users of lha should update to this updated package Solution : http://www.fedoranews.org/updates/FEDORA-2004-295.shtml Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

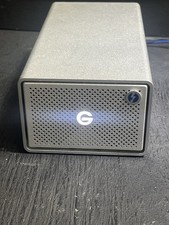
G-Technology G-RAID 24TB Dual-Drive External HDD TB3 USB 3.1 7200RPM Silver
$299.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
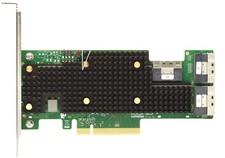
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
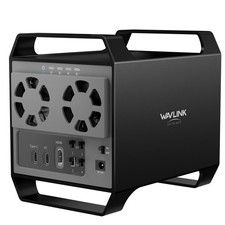
2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99
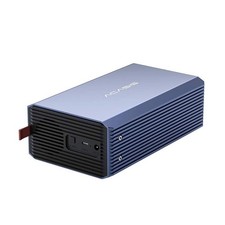
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
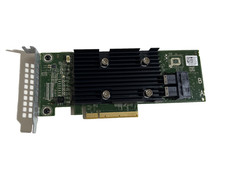
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
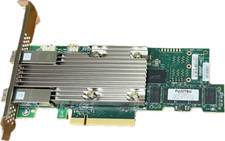
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |