|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 2 2004-287: gdk-pixbuf Vulnerability Assessment Details
|
Fedora Core 2 2004-287: gdk-pixbuf |
||
|
Check for the version of the gdk-pixbuf package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-287 (gdk-pixbuf). The gdk-pixbuf package contains an image loading library used with the GNOME GUI desktop environment. The GdkPixBuf library provides image loading facilities, the rendering of a GdkPixBuf into various formats (drawables or GdkRGB buffers), and a cache interface. Update Information: During testing of a previously fixed flaw in Qt (CVE-2004-0691), a flaw was discovered in the BMP image processor of gdk-pixbuf. A possible hacker could create a carefully crafted BMP file which would cause an application to enter an infinite loop and not respond to user input when the file was opened by a victim. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0753 to this issue. During a security audit, Chris Evans discovered a stack and a heap overflow in the XPM image decoder. A possible hacker could create a carefully crafted XPM file which could cause an application linked with gtk2 to crash or possibly execute arbitrary code when the file was opened by a victim. (CVE-2004-0782, CVE-2004-0783) Chris Evans also discovered an integer overflow in the ICO image decoder. A possible hacker could create a carefully crafted ICO file which could cause an application linked with gtk2 to crash when the file is opened by a victim. (CVE-2004-0788) Solution : http://www.fedoranews.org/updates/FEDORA-2004-287.shtml Network Security Threat Level: High Networks Security ID: 11195 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

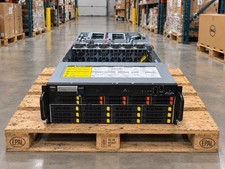
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
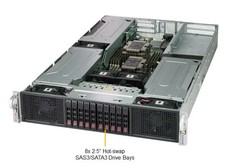
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |