|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 2 2004-160: squirrelmail Vulnerability Assessment Details
|
Fedora Core 2 2004-160: squirrelmail |
||
|
Check for the version of the squirrelmail package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-160 (squirrelmail). SquirrelMail is a standards-based webmail package written in PHP4. It includes built-in pure PHP support for the IMAP and SMTP protocols, and all pages render in pure HTML 4.0 (with no Javascript) for maximum compatibility across browsers. It has very few requirements and is very easy to configure and install. SquirrelMail has all the functionality you would want from an email client, including strong MIME support, address books, and folder manipulation. Update Information: An SQL injection flaw was found in SquirrelMail version 1.4.2 and earlier. If SquirrelMail is configured to store user addressbooks in the database, a remote attacker could use this flaw to execute arbitrary SQL statements. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-0521 to this issue. A number of cross-site scripting (XSS) flaws in SquirrelMail version 1.4.2 and earlier could permit remote attackers to execute scripts as other web users. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2004-0519 and CVE-2004-0520 to these issues. This update includes the SquirrelMail version 1.4.3a which is not vulnerable to these issues. Solution : http://www.fedoranews.org/updates/FEDORA-2004-160.shtml Network Security Threat Level: High Networks Security ID: 10397 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

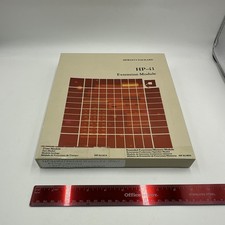
Vintage HP-41 Extension Module Box Set - HP 82182A Time Module Complete Lot
$185.00
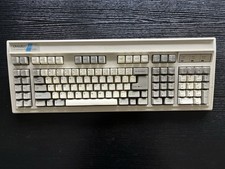
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
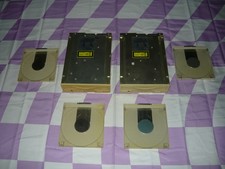
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
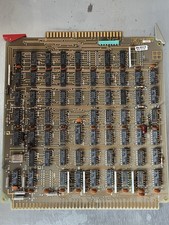
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
RARE Vintage Chicony KB-5181 Mechanical Keyboard Monterey Blue SMK Switches
$65.00
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
Vintage Magnetic Peripherals MPI BR8B1A 5.25" Floppy Disk Drive 77711800 CDC
$89.66
|
||
|
No Discussions have been posted on this vulnerability. |