|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-292: kdebase Vulnerability Assessment Details
|
Fedora Core 1 2004-292: kdebase |
||
|
Check for the version of the kdebase package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-292 (kdebase). Core applications for the K Desktop Environment. Included are: kdm (replacement for xdm), kwin (window manager), konqueror (filemanager, web browser, ftp client, ...), konsole (xterm replacement), kpanel (application starter and desktop pager), kaudio (audio server), kdehelp (viewer for kde help files, info and man pages), kthememgr (system for managing alternate theme packages) plus other KDE components (kcheckpass, kikbd, kscreensaver, kcontrol, kfind, kfontmanager, kmenuedit). Update Information: Andrew Tuitt reported that versions of KDE up to and including 3.2.3 create temporary directories with predictable names. A local attacker could prevent KDE applications from functioning correctly, or overwrite files owned by other users by creating malicious symlinks. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-0689 to this issue. WESTPOINT internet reconnaissance services has discovered that the KDE web browser Konqueror permits websites to set cookies for certain country specific secondary top level domains. A possible hacker within one of the affected domains could construct a cookie which would be sent to all other websites within the domain leading to a session fixation attack. This issue does not affect popular domains such as .co.uk, .co.in, or .com. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-0721 to this issue. A frame injection spoofing vulnerability has been discovered in the Konqueror web browser. This issue could permit a malicious website to show arbitrary content in a named frame of a different browser window. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-0746 to this issue. All users of KDE are advised to upgrade to these packages, which contain backported patches from the KDE team for these issues. Solution : http://www.fedoranews.org/updates/FEDORA-2004-292.shtml Network Security Threat Level: High Networks Security ID: 11186 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

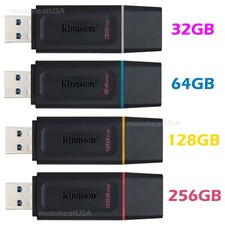
Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
SanDisk Ultra Luxe USB 3.1 Flash Drive – 5 Pack | Premium Metal USB Flash Drives
$59.99
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$269.10
Microsoft Windows 11 Pro 64bit - New Sealed – Flash USB 1 PC
$49.99
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
USB Type-A Flash Drive Metal Memory Stick High Speed USB Drive 128GB 256GB 512GB
$8.47
Wholesale 5/10/100PCS 1MB- 64GB USB 2.0 Flash Drive Memory Stick Jump Drive Lot
$280.00
LOT 10x SanDisk 32GB ULTRA USB 3.0 flash drive SDCZ48-032G 32 GB read 100 MB/s
$39.80
2021 Full Version Office Professional Plus for 1 PC Flash USB Drive
$59.99
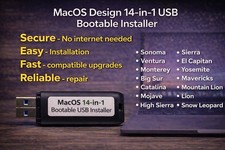
128GB USB 14-in-1 MacOS bootable Installer repair recovery tech support service
$39.99
|
||
|
No Discussions have been posted on this vulnerability. |