|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-126: cvs Vulnerability Assessment Details
|
Fedora Core 1 2004-126: cvs |
||
|
Check for the version of the cvs package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-126 (cvs). CVS (Concurrent Version System) is a version control system that can record the history of your files (usually, but not always, source code). CVS only stores the differences between versions, instead of every version of every file you have ever created. CVS also keeps a log of who, when, and why changes occurred. CVS is very helpful for managing releases and controlling the concurrent editing of source files among multiple authors. Instead of providing version control for a collection of files in a single directory, CVS provides version control for a hierarchical collection of directories consisting of revision controlled files. These directories and files can then be combined together to form a software release. Update Information: Stefan Esser discovered a flaw in cvs where malformed 'Entry' lines could cause a heap overflow. A possible hacker who has access to a CVS server could use this flaw to execute arbitrary code under the UID which the CVS server is executing. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0396 to this issue. This update includes a patch by Derek Price, based on a patch by Stefan Esser, which corrects this flaw. Solution : http://www.fedoranews.org/updates/FEDORA-2004-126.shtml Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

AMD Ryzen 5 5500 Processor ( read Description)
$59.00
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
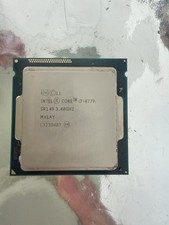
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
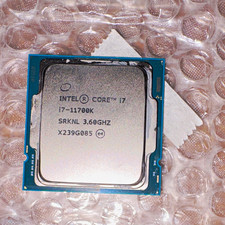
Intel Core i7-11700K 3.60GHz 11th Gen CPU Processor MPN SRKNL X239G085
$140.00
|
||
|
No Discussions have been posted on this vulnerability. |