|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-101: kernel Vulnerability Assessment Details
|
Fedora Core 1 2004-101: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-101 (kernel). The kernel package contains the Linux kernel (vmlinuz), the core of your Fedora Core Linux operating system. The kernel handles the basic functions of the operating system: memory allocation, process allocation, device input and output, etc. Update Information: iDefense reported a buffer overflow flaw in the ISO9660 filesystem code. A possible hacker could create a malicious filesystem in such a way that they could gain root rights if that filesystem is mounted. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0109 to this issue. Solar Designer from OpenWall discovered a minor information leak in the ext3 filesystem code due to the lack of initialization of journal descriptor blocks. This flaw has only minor security implications and exploitation requires privileged access to the raw device. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0133 to this issue. These packages also contain an updated fix with additional checks for issues in the R128 Direct Render Infrastructure. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0003 to this issue. Additionally, additional hardening of the mremap function was applied to prevent a potential local denial of service attack. The low latency patch applied in previous kernels has also been found to cause stability problems under certain conditions. It has been disabled in this update whilst further investigation occurs. Solution : http://www.fedoranews.org/updates/FEDORA-2004-101.shtml Network Security Threat Level: High Networks Security ID: 10151, 9570 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
Lenovo IdeaPad S340-15IWL Laptop 15.6" Intel Core i3-8145U 8GB RAM 256GB SSD
$126.65
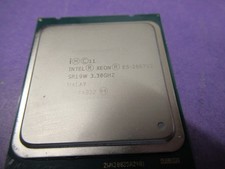
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 7800X3D 4.20GHz Quad Core 100-000000510 8 Thread AM4
$279.99
AMD Ryzen 7 5700G 8-Core 16-Thread 4.6GHz Max Boost, 3.8 GHz Base
$170.00
$600.00
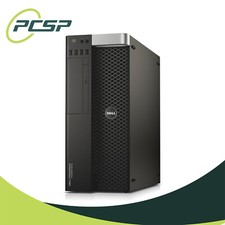
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |