|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-092: tcpdump Vulnerability Assessment Details
|
Fedora Core 1 2004-092: tcpdump |
||
|
Check for the version of the tcpdump package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-092 (tcpdump). Tcpdump is a command-line tool for monitoring network traffic. Tcpdump can capture and display the packet headers on a particular network interface or on all interfaces. Tcpdump can display all of the packet headers, or just the ones that match particular criteria. Install tcpdump if you need a program to monitor network traffic. Update Information: Updated tcpdump, libpcap, and arpwatch packages fix vulnerabilities in ISAKMP and RADIUS parsing. Tcpdump is a command-line tool for monitoring network traffic. George Bakos discovered flaws in the ISAKMP decoding routines of tcpdump versions prior to 3.8.1. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0989 to this issue. Jonathan Heusser discovered an additional flaw in the ISAKMP decoding routines for tcpdump 3.8.1 and earlier. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0057 to this issue. Jonathan Heusser discovered a flaw in the print_attr_string function in the RADIUS decoding routines for tcpdump 3.8.1 and earlier. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0055 to this issue. Remote attackers could potentially exploit these issues by sending carefully-crafted packets to a victim. If the victim uses tcpdump, these pakets could result in a denial of service, or possibly execute arbitrary code as the 'pcap' user. Users of tcpdump are advised to upgrade to these erratum packages, which contain backported security patches and are not vulnerable to these issues. Solution : http://www.fedoranews.org/updates/FEDORA-2004-092.shtml Network Security Threat Level: High Networks Security ID: 9423 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

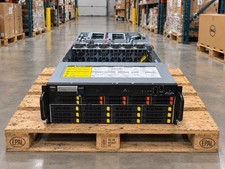
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
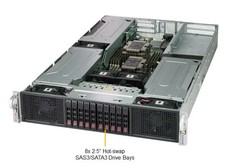
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |