|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-079: kernel Vulnerability Assessment Details
|
Fedora Core 1 2004-079: kernel |
||
|
Check for the version of the kernel package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-079 (kernel). The kernel package contains the Linux kernel (vmlinuz), the core of your Fedora Core Linux operating system. The kernel handles the basic functions of the operating system: memory allocation, process allocation, device input and output, etc. Update Information: Paul Starzetz discovered a flaw in return value checking in mremap() in the Linux kernel versions 2.4.24 and previous that may permit a local attacker to gain root rights. No exploit is currently available however this issue is exploitable. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0077 to this issue. Arjan van de Ven discovered a flaw in ncp_lookup() in ncpfs that could permit local privilege escalation. ncpfs is only used to permit a system to mount volumes of NetWare servers or print to NetWare printers. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0010 to this issue. All users are advised to upgrade to these errata packages, which contain backported security patches that correct these issues. Red Hat would like to thank Paul Starzetz from ISEC for reporting the issue CVE-2004-0077. Solution : http://www.fedoranews.org/updates/FEDORA-2004-079.shtml Network Security Threat Level: High Networks Security ID: 9686, 9691 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

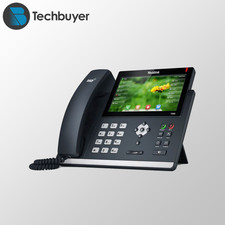
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
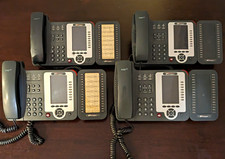
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
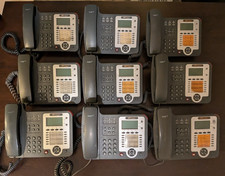
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
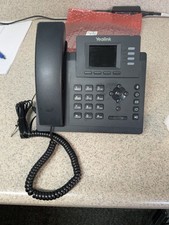
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
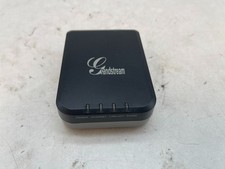
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
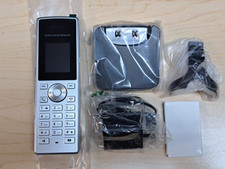
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
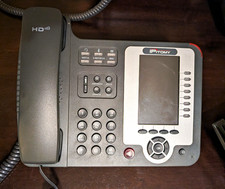
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |