|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Fedora Local Security Checks >> Fedora Core 1 2004-069: XFree86 Vulnerability Assessment Details
|
Fedora Core 1 2004-069: XFree86 |
||
|
Check for the version of the XFree86 package Detailed Explanation for this Vulnerability Assessment The remote host is missing the patch for the advisory FEDORA-2004-069 (XFree86). XFree86 is an open source implementation of the X Window System. It provides the basic low level functionality which full fledged graphical user interfaces (GUIs) such as GNOME and KDE are designed upon. Update Information: Updated XFree86 packages that fix a privilege escalation vulnerability are now available. XFree86 is an implementation of the X Window System, providing the core graphical user interface and video drivers. iDefense discovered two buffer overflows in the parsing of the 'font.alias' file. A local attacker could exploit this vulnerability by creating a carefully-crafted file and gaining root rights. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2004-0083 and CVE-2004-0084 to these issues. Additionally David Dawes discovered additional flaws in reading font files. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0106 to these issues. All users of XFree86 are advised to upgrade to these erratum packages, which contain a backported fix and are not vulnerable to these issues. Red Hat would like to thank David Dawes from XFree86 for the patches and notification of these issues. Solution : http://www.fedoranews.org/updates/FEDORA-2004-069.shtml Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |


Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
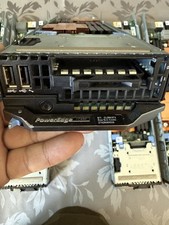
Dell PowerEdge FC430 Blade Server 2x Xeon E5-2630v4 20 Cores FX2 FX2s No RAM/HDD
$119.99
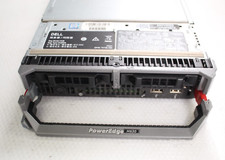
Dell PowerEdge M630 Blade Server 2x Xeon E5-2680 v4, 2F3MP , 4GDP5 ,R10KJ ,JVFVR
$95.20
Dell PowerEdge M620 Blade Server 2x Xeon E5-2680v2 2.8ghz 20-Cores | 128GB
$149.99
NETAPP HCI NAF-1701 SuperMicro Server 4X BLADE H410C 8X GOLD 5120 4 NODE SERVER
$1499.97
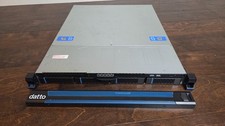
Datto S4P10 1U Blade Rack Server Intel Xeon D-2143IT 2.20GHz 48GB DDR4 4-Bay PSU
$229.95
Dell Poweredge C6400 24x 2.5’’ 2x 2400W 4x C6420 Nodes H330 | 2x SFP | 8x Trays
$799.99
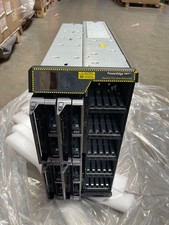
Dell PowerEdge VRTX 2.5"x25 Bay Blade Enclosure 4x1600W + 4X M640 (4X Blades)
$1599.99
Dell PowerEdge M640 Blade Barebone Server Dell P/N: HHB006 Tested Working
$149.99
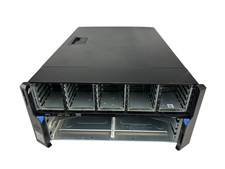
Dell Poweredge VRTX 25Bay 2.5" 2x PERC 8, 2xCMC, I/O 1GB Pass Through, 4x PS
$578.08
|
||
|
No Discussions have been posted on this vulnerability. |