|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> SMTP problems >> Debian GNU/Linux Sendmail Default SASL Password Vulnerability Assessment Details
|
Debian GNU/Linux Sendmail Default SASL Password |
||
|
Checks SMTP authentication Detailed Explanation for this Vulnerability Assessment The remote host is running a Sendmail server with a default SASL password of 'sendmail' / 'sendmailpwd'. A spammer may use this account to use the remote server as a spam relay for the internet. See also : http://www.debian.org/security/2004/dsa-554 Solution : Disable this account as soon as possible Network Security Threat Level: High Networks Security ID: 11262 Vulnerability Assessment Copyright: This script is Copyright (C) 2004-2007 Tenable Network Security |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
HGST 0F23072 Deskstar NAS 6TB SATA III 7200RPM 128MB 3.5in HDD
$84.99
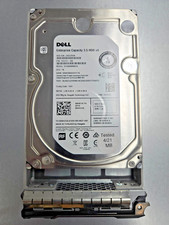
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
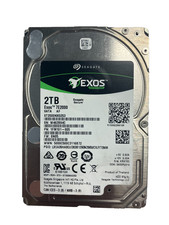
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
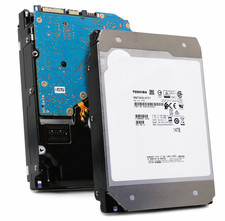
Toshiba 14TB MG07 MG07ACA14TEY 7.2K RPM SATA 6Gb/s 512e 3.5" Enterprise HDD
$339.00
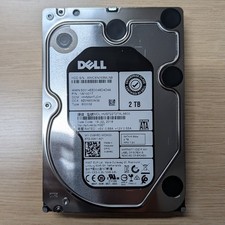
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95

Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
|
||
|
No Discussions have been posted on this vulnerability. |