|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA967] DSA-967-1 elog Vulnerability Assessment Details
|
[DSA967] DSA-967-1 elog |
||
|
DSA-967-1 elog Detailed Explanation for this Vulnerability Assessment Several security problems have been found in elog, an electronic logbook to manage notes. The Common Vulnerabilities and Exposures Project identifies the following problems: "GroundZero Security" discovered that elog insufficiently checks the size of a buffer used for processing URL parameters, which might lead to the execution of arbitrary code. It was discovered that elog contains a directory traveral vulnerability in the processing of "../" sequences in URLs, which might lead to information disclosure. The code to write the log file contained a format string vulnerability, which might lead to the execution of arbitrary code. Overly long revision attributes might trigger a crash due to a buffer overflow. The code to write the log file does not enforce bounds checks properly, which might lead to the execution of arbitrary code. elog emitted different errors messages for invalid passwords and invalid users, which permits a possible hacker to probe for valid user names. A possible hacker could be driven into infinite redirection with a crafted "fail" request, which has denial of service potential. The old stable distribution (woody) does not contain elog packages. For the stable distribution (sarge) these problems have been fixed in version 2.5.7+r1558-4+sarge2. For the unstable distribution (sid) these problems have been fixed in version 2.6.1+r1642-1. We recommend that you upgrade your elog package. Solution : http://www.debian.org/security/2006/dsa-967 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
Samsung 32GB (2x16GB) DDR5-5600 SODIMM 32GB (2x16GB) PC5-4800 RAM Laptop
$750.00
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Corsair Vengeance DDR3 8GB 16GB 32GB 1866MHz PC3-14900 Desktop RAM Memory DIMM
$85.00
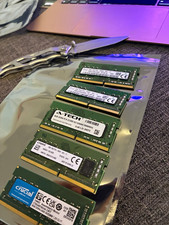
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |