|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA956] DSA-956-1 lsh-server Vulnerability Assessment Details
|
[DSA956] DSA-956-1 lsh-server |
||
|
DSA-956-1 lsh-server Detailed Explanation for this Vulnerability Assessment Stefan Pfetzing discovered that lshd, a Secure Shell v2 (SSH2) protocol server, leaks a couple of file descriptors, related to the randomness generator, to user shells which are started by lshd. A local attacker can truncate the server's seed file, which may prevent the server from starting, and with some more effort, maybe also crack session keys. After applying this update, you should remove the server's seed file (/var/spool/lsh/yarrow-seed-file) and then regenerate it with "lsh-make-seed --server" as root. For security reasons, lsh-make-seed really needs to be run from the console of the system you are running it on. If you run lsh-make-seed using a remote shell, the timing information lsh-make-seed uses for its random seed creation is likely to be screwed. If need be, you can generate the random seed on a different system than that which it will eventually be on, by installing the lsh-utils package and running "lsh-make-seed -o my-other-server-seed-file". You may then transfer the seed to the destination system as using a secure connection. The old stable distribution (woody) may not be affected by this problem. For the stable distribution (sarge) this problem has been fixed in version 2.0.1-3sarge1. For the unstable distribution (sid) this problem has been fixed in version 2.0.1cdbs-4. We recommend that you upgrade your lsh-server package. Solution : http://www.debian.org/security/2006/dsa-956 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
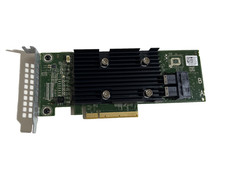
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
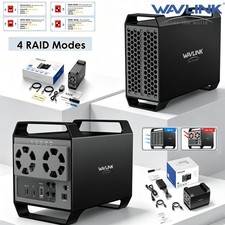
WAVLINK RAID 2 Bay Hard Drive Docking Station SATA 2.5/3.5'' SSD HDD Enclosure
$119.99
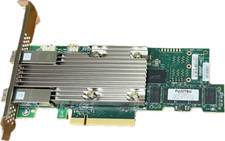
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |