|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA946] DSA-946-2 sudo Vulnerability Assessment Details
|
[DSA946] DSA-946-2 sudo |
||
|
DSA-946-2 sudo Detailed Explanation for this Vulnerability Assessment The former correction to vulnerabilities in the sudo package worked fine but were too strict for some environments. Therefore we have reviewed the changes again and permited some environment variables to go back into the privileged execution environment. Hence, this update. The configuration option "env_reset" is now activated by default. It will preserve only the environment variables HOME, LOGNAME, PATH, SHELL, TERM, DISPLAY, XAUTHORITY, XAUTHORIZATION, LANG, LANGUAGE, LC_*, and USER in addition to the separate SUDO_* variables. For completeness please find below the original advisory text: It has been discovered that sudo, a privileged program, that provides limited super user rights to specific users, passes several environment variables to the program that runs with elevated rights. In the case of include paths (e.g. for Perl, Python, Ruby or other scripting languages) this can cause arbitrary code to be executed as privileged user if the attacker points to a manipulated version of a system library. This update alters the former behaviour of sudo and limits the number of supported environment variables to LC_*, LANG, LANGUAGE and TERM. Additional variables are only passed through when set as env_check in /etc/sudoers, which might be required for some scripts to continue to work. For the old stable distribution (woody) this problem has been fixed in version 1.6.6-1.6. For the stable distribution (sarge) this problem has been fixed in version 1.6.8p7-1.4. For the unstable distribution (sid) the same behaviour will be implemented soon. We recommend that you upgrade your sudo package. For unstable "Defaults = env_reset" need to be added to /etc/sudoers manually. Solution : http://www.debian.org/security/2006/dsa-946 Network Security Threat Level: High Networks Security ID: 16184 Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

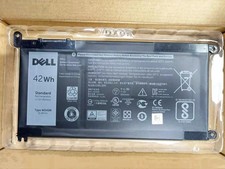
OEM Genuine 42Wh WDX0R For DELL Inspiron WDXOR Battery 15 5567 5568 13 5368 7368
$22.99
OEM 68Wh 3HWPP Battery For Dell Latitude 5401 5501 5410 5510 E5411 E5511
$28.99
Genuine OEM 6GTPY 97Wh Battery for Dell XPS 15 7590, 9550 Series 5XJ28 GPM03 New
$33.50
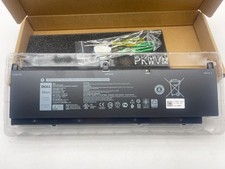
OEM Genuine 95WH PKWVM C903V Battery 7550 For Dell Precision CR72X 17C06 447VR
$37.40
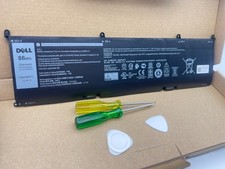
OEM Genuine 86WH 69KF2 Battery For Dell XPS 15 9500 Precision 5550 M59JH M15 M17
$45.49
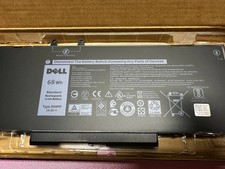
OEM 68Wh 3HWPP Battery For Dell Latitude 5401 5411 15 5501 5511 Precision 3541
$35.78
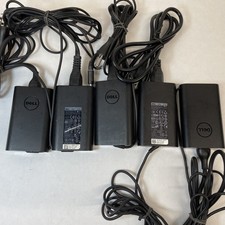
Lot of 5 Dell OEM 65W 7.4mm 19.5V 3.34A AC Adapters Mixed Models B Grade
$36.99
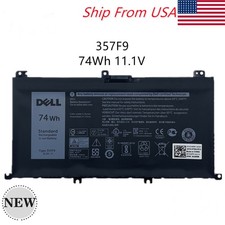
OEM 74WH 357F9 Battery For Dell Inspiron 15 7559 i7559 7557 i7557 5577 7567 5576
$26.99
Genuine OEM 63Wh 7FMXV Battery For Dell Latitude 5320 7320 7420 7520 4M1JN TN2GY
$32.99
New Genuine OEM Dell Latitude 5420 5520 3560 4 Cell Laptop Battery RJ40G M033W
$49.95
|
||
|
No Discussions have been posted on this vulnerability. |