|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA921] DSA-921-1 kernel-source-2.4.27 Vulnerability Assessment Details
|
[DSA921] DSA-921-1 kernel-source-2.4.27 |
||
|
DSA-921-1 kernel-source-2.4.27 Detailed Explanation for this Vulnerability Assessment Several local and remote vulnerabilities have been discovered in the Linux kernel that may lead to a denial of service or the execution of arbitrary code. The Common Vulnerabilities and Exposures project identifies the following problems: Alexander Nyberg discovered that the ptrace() system call does not properly verify addresses on the amd64 architecture which can be exploited by a local attacker to crash the kernel. A problem in the offset handling in the xattr file system code for ext3 has been discovered that may permit users on 64-bit systems that have access to an ext3 filesystem with extended attributes to cause the kernel to crash. A vulnerability has been discovered in the ptrace() system call on the amd64 architecture that permits a local attacker to cause the kernel to crash. A vulnerability has been discovered in the stack segment fault handler that could permit a local attacker to cause a stack exception that will lead the kernel to crash under certain circumstances. Ilja van Sprundel discovered a race condition in the IA32 (x86) compatibility execve() systemcall for amd64 and IA64 that permits local attackers to cause the kernel to panic and possibly execute arbitrary code. Balazs Scheidler discovered that a local attacker could call setsockopt() with an invalid xfrm_user policy message which would cause the kernel to write beyond the boundaries of an array and crash. Vladimir Volovich discovered a bug in the zlib routines which are also present in the Linux kernel and permits remote attackers to crash the kernel. Another vulnerability has been discovered in the zlib routines which are also present in the Linux kernel and permits remote attackers to crash the kernel. A null pointer dereference in ptrace when tracing a 64-bit executable can cause the kernel to crash. Andreas Gruenbacher discovered a bug in the ext2 and ext3 file systems. When data areas are to be shared among two inodes not all information were compared for equality, which could expose wrong ACLs for files. Chad Walstrom discovered that the ipt_recent kernel module to stop SSH bruteforce attacks could cause the kernel to crash on 64-bit architectures. An error in the NAT code permits remote attackers to cause a denial of service (memory corruption) by causing two packets for the same protocol to be NATed at the same time, which leads to memory corruption. The following matrix explains which kernel version for which architecture fix the problems mentioned above: We recommend that you upgrade your kernel package immediately and reboot the machine. Solution : http://www.debian.org/security/2005/dsa-921 Network Security Threat Level: High Networks Security ID: 14477 Vulnerability Assessment Copyright: This script is (C) 2006 Michel Arboi |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
SolarFlare XtremeScale X2522-25G-PLUS Dual Port 25G SFP28 PCI-E 3.1 x8 NIC FH LP
$899.99

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
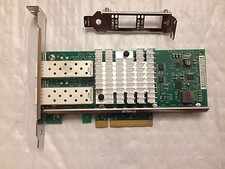
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
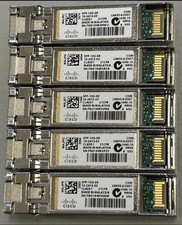
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |