|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA868] DSA-868-1 mozilla-thunderbird Vulnerability Assessment Details
|
[DSA868] DSA-868-1 mozilla-thunderbird |
||
|
DSA-868-1 mozilla-thunderbird Detailed Explanation for this Vulnerability Assessment Several security-related problems have been discovered in Mozilla and derived programs. Some of the following problems don't exactly apply to Mozilla Thunderbird, even though the code is present. In order to keep the codebase in sync with upstream it has been altered nevertheless. The Common Vulnerabilities and Exposures project identifies the following problems: Tom Ferris discovered a bug in the IDN hostname handling of Mozilla that permits remote attackers to cause a denial of service and possibly execute arbitrary code via a hostname with dashes. A buffer overflow permits remote attackers to execute arbitrary code via an XBM image file that ends in a large number of spaces instead of the expected end tag. Mats Palmgren discovered a buffer overflow in the Unicode string parser that permits a specially crafted Unicode sequence to overflow a buffer and cause arbitrary code to be executed. Remote attackers could spoof HTTP headers of XML HTTP requests via XMLHttpRequest and possibly use the client to exploit vulnerabilities in servers or proxies. Remote attackers could spoof DOM objects via an XBL control that implements an internal XPCOM interface. Georgi Guninski discovered an integer overflow in the JavaScript engine that might permit remote attackers to execute arbitrary code. Remote attackers could execute Javascript code with chrome rights via an about: page such as about:mozilla. Remote attackers could spawn windows without user interface components such as the address and status bar that could be used to conduct spoofing or phishing attacks. Peter Zelezny discovered that shell metacharacters are not properly escaped when they are passed to a shell script and permit the execution of arbitrary commands, e.g. when a malicious URL is automatically copied from another program into Mozilla as default browser. For the stable distribution (sarge) these problems have been fixed in version 1.0.2-2.sarge1.0.7. For the unstable distribution (sid) these problems have been fixed in version 1.0.7-1. We recommend that you upgrade your mozilla-thunderbird package. Solution : http://www.debian.org/security/2005/dsa-868 Network Security Threat Level: High Networks Security ID: 14784 Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

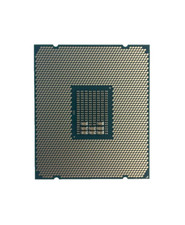
INTEL XEON E5-2680V4 SR2N7 2.40GHZ CPU
$11.00
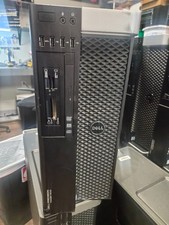
Dell Precision Tower 7810 Xeon E5-2630 v3 @ 2.40GHz , 32GB Ram, NO HDD, NO OS
$239.99
Dell Precision T7820 2x Xeon Silver 4114 2.20GHz 950W No RAM GPU HDD 4x SATA
$350.48
Dell Precision T5820 950W Workstation 4.00GHz W-2125 No RAM/ GPU/ HDD/ OS
$144.98
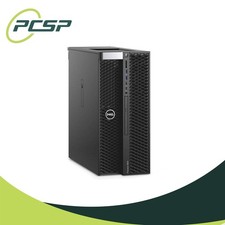
Dell Precision T5820 Workstation 3.70GHz W-2135 No RAM/ GPU/ HDD/ OS
$179.98
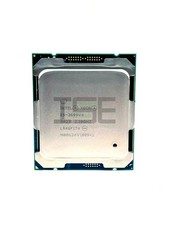
Intel Xeon E5-2699 V4 2.20GHz 55M 22-CORES LGA2011-3 Server Processor 145W SR2JS
$84.49
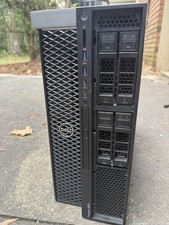
DELL Precision 5820 Workstation Xeon W-2123 3.6ghz/NO RAM/NO SSD/P400 Vid
$139.99
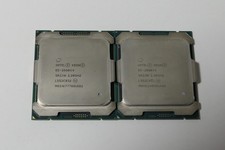
Matched Pair _ Intel Xeon E5-2698 V4 2.2GHz 20-Core Processor CPU LGA2011 SR2JW
$94.99

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00
|
||
|
No Discussions have been posted on this vulnerability. |