|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA781] DSA-781-1 mozilla-thunderbird Vulnerability Assessment Details
|
[DSA781] DSA-781-1 mozilla-thunderbird |
||
|
DSA-781-1 mozilla-thunderbird Detailed Explanation for this Vulnerability Assessment Several problems have been discovered in Mozilla Thunderbird, the standalone mail client of the Mozilla suite. The Common Vulnerabilities and Exposures project identifies the following problems: Remote attackers could read portions of heap memory into a Javascript string via the lambda replace method. The Javascript interpreter could be tricked to continue execution at the wrong memory address, which may permit attackers to cause a denial of service (application crash) and possibly execute arbitrary code. Remote attackers could override certain properties or methods of DOM nodes and gain rights. Remote attackers could override certain properties or methods due to missing proper limitation of Javascript eval and Script objects and gain rights. XML scripts ran even when Javascript disabled. Missing input sanitising of InstallVersion.compareTo() can cause the application to crash. Remote attackers could steal sensitive information such as cookies and passwords from web sites by accessing data in alien frames. Remote attackers could modify certain tag properties of DOM nodes that could lead to the execution of arbitrary script or code. The Mozilla browser family does not properly clone base objects, which permits remote attackers to execute arbitrary code. The old stable distribution (woody) is not affected by these problems since it does not contain Mozilla Thunderbird packages. For the stable distribution (sarge) these problems have been fixed in version 1.0.2-2.sarge1.0.6. For the unstable distribution (sid) these problems have been fixed in version 1.0.6-1. We recommend that you upgrade your Mozilla Thunderbird package. Solution : http://www.debian.org/security/2005/dsa-781 Network Security Threat Level: High Networks Security ID: 14242, 14242 Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

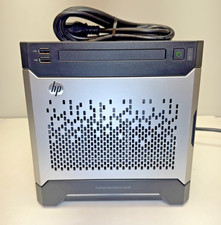
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
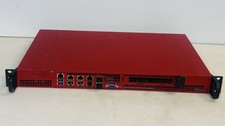
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
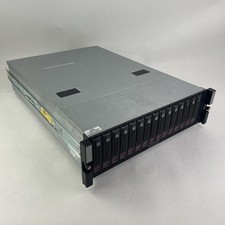
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
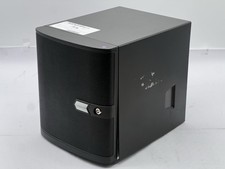
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |