|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA764] DSA-764-1 cacti Vulnerability Assessment Details
|
[DSA764] DSA-764-1 cacti |
||
|
DSA-764-1 cacti Detailed Explanation for this Vulnerability Assessment Several vulnerabilities have been discovered in cacti, a round-robin database (RRD) tool that helps create graphs from database information. The Common Vulnerabilities and Exposures Project identifies the following problems: Maciej Piotr Falkiewicz and an anonymous researcher discovered an input validation bug that permits a possible hacker to include arbitrary PHP code from remote sites which will permit the execution of arbitrary code on the server running cacti. Due to missing input validation cacti permits a remote attacker to insert arbitrary SQL statements. Maciej Piotr Falkiewicz discovered an input validation bug that permits a possible hacker to include arbitrary PHP code from remote sites which will permit the execution of arbitrary code on the server running cacti. Stefan Esser discovered that the update for the above mentioned vulnerabilities does not perform proper input validation to protect against common attacks. Stefan Esser discovered that the update for CVE-2005-1525 permits remote attackers to modify session information to gain rights and disable the use of addslashes to protect against SQL injection. For the old stable distribution (woody) these problems have been fixed in version 0.6.7-2.5. For the stable distribution (sarge) these problems have been fixed in version 0.8.6c-7sarge2. For the unstable distribution (sid) these problems have been fixed in version 0.8.6f-2. We recommend that you upgrade your cacti package. Solution : http://www.debian.org/security/2005/dsa-764 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |

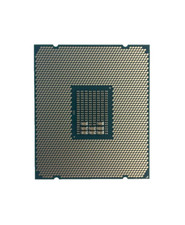
INTEL XEON E5-2680V4 SR2N7 2.40GHZ CPU
$11.00
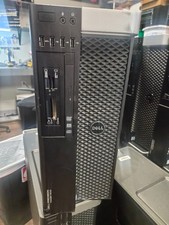
Dell Precision Tower 7810 Xeon E5-2630 v3 @ 2.40GHz , 32GB Ram, NO HDD, NO OS
$239.99
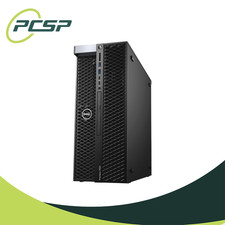
Dell Precision T7820 2x Xeon Silver 4114 2.20GHz 950W No RAM GPU HDD 4x SATA
$350.48
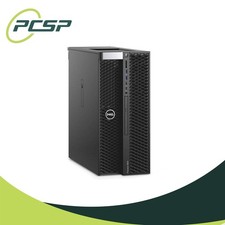
Dell Precision T5820 950W Workstation 4.00GHz W-2125 No RAM/ GPU/ HDD/ OS
$144.98
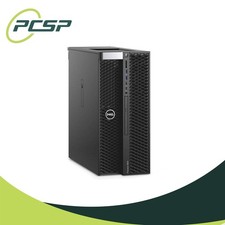
Dell Precision T5820 Workstation 3.70GHz W-2135 No RAM/ GPU/ HDD/ OS
$179.98
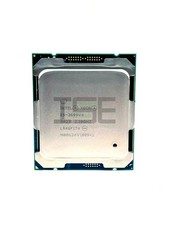
Intel Xeon E5-2699 V4 2.20GHz 55M 22-CORES LGA2011-3 Server Processor 145W SR2JS
$84.49
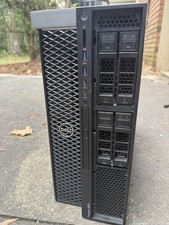
DELL Precision 5820 Workstation Xeon W-2123 3.6ghz/NO RAM/NO SSD/P400 Vid
$139.99
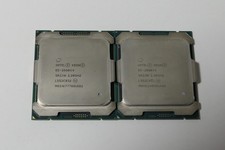
Matched Pair _ Intel Xeon E5-2698 V4 2.2GHz 20-Core Processor CPU LGA2011 SR2JW
$94.99

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |