|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Debian Local Security Checks >> [DSA757] DSA-757-1 krb5 Vulnerability Assessment Details
|
[DSA757] DSA-757-1 krb5 |
||
|
DSA-757-1 krb5 Detailed Explanation for this Vulnerability Assessment Daniel Wachdorf reported two problems in the MIT krb5 distribution used for network authentication. First, the KDC program from the krb5-kdc package can corrupt the heap by trying to free memory which has already been freed on receipt of a certain TCP connection. This vulnerability can cause the KDC to crash, leading to a denial of service. [CVE-2005-1174] Second, under certain rare circumstances this type of request can lead to a buffer overflow and remote code execution. [CVE-2005-1175] Additionally, Magnus Hagander reported another problem in which the krb5_recvauth function can in certain circumstances free previously freed memory, potentially leading to the execution of remote code. [CVE-2005-1689] All of these vulnerabilities are believed difficult to exploit, and no exploits have yet been discovered. For the old stable distribution (woody), these problems have been fixed in version 1.2.4-5woody10. Note that woody's KDC does not have TCP support and is not vulnerable to CVE-2005-1174. For the stable distribution (sarge), these problems have been fixed in version 1.3.6-2sarge2. For the unstable distribution (sid), these problems have been fixed in version 1.3.6-4. We recommend that you upgrade your krb5 package. Solution : http://www.debian.org/security/2005/dsa-757 Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is (C) 2007 Michel Arboi |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
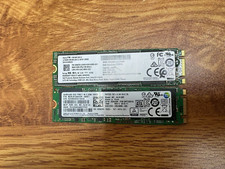
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
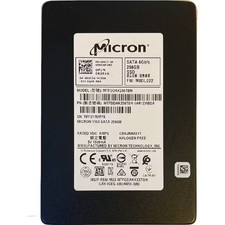
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
|
||
|
No Discussions have been posted on this vulnerability. |